What Happens Next
Your path from today to audit-ready: clear, simple, and fully supported.
Key HIPAA Terms Referenced in This Process
Security Risk Assessment (SRA)
A systematic look at threats and weaknesses that could expose electronic Protected Health Information (ePHI). Required under 45 CFR § 164.308(a)(1), the SRA is the starting point of every HIPAA program. It is also the first thing OCR asks for during an investigation.
Protected Health Information (PHI)
Health information tied to a specific person. This includes medical records, billing data, and insurance details held by a covered entity or business associate. When stored or sent electronically, it is called ePHI.
Business Associate Agreement (BAA)
A required written contract between a covered entity and any vendor that handles PHI. The BAA spells out what the vendor can do with PHI, what safeguards they must use, and how they must report breaches as specified in 45 CFR § 164.502(e).
Privacy Officer
The person your organization picks to own HIPAA privacy policies. Required under 45 CFR § 164.530(a)(1), the Privacy Officer is your main compliance contact. They are the first user set up in the One Guy Consulting portal.
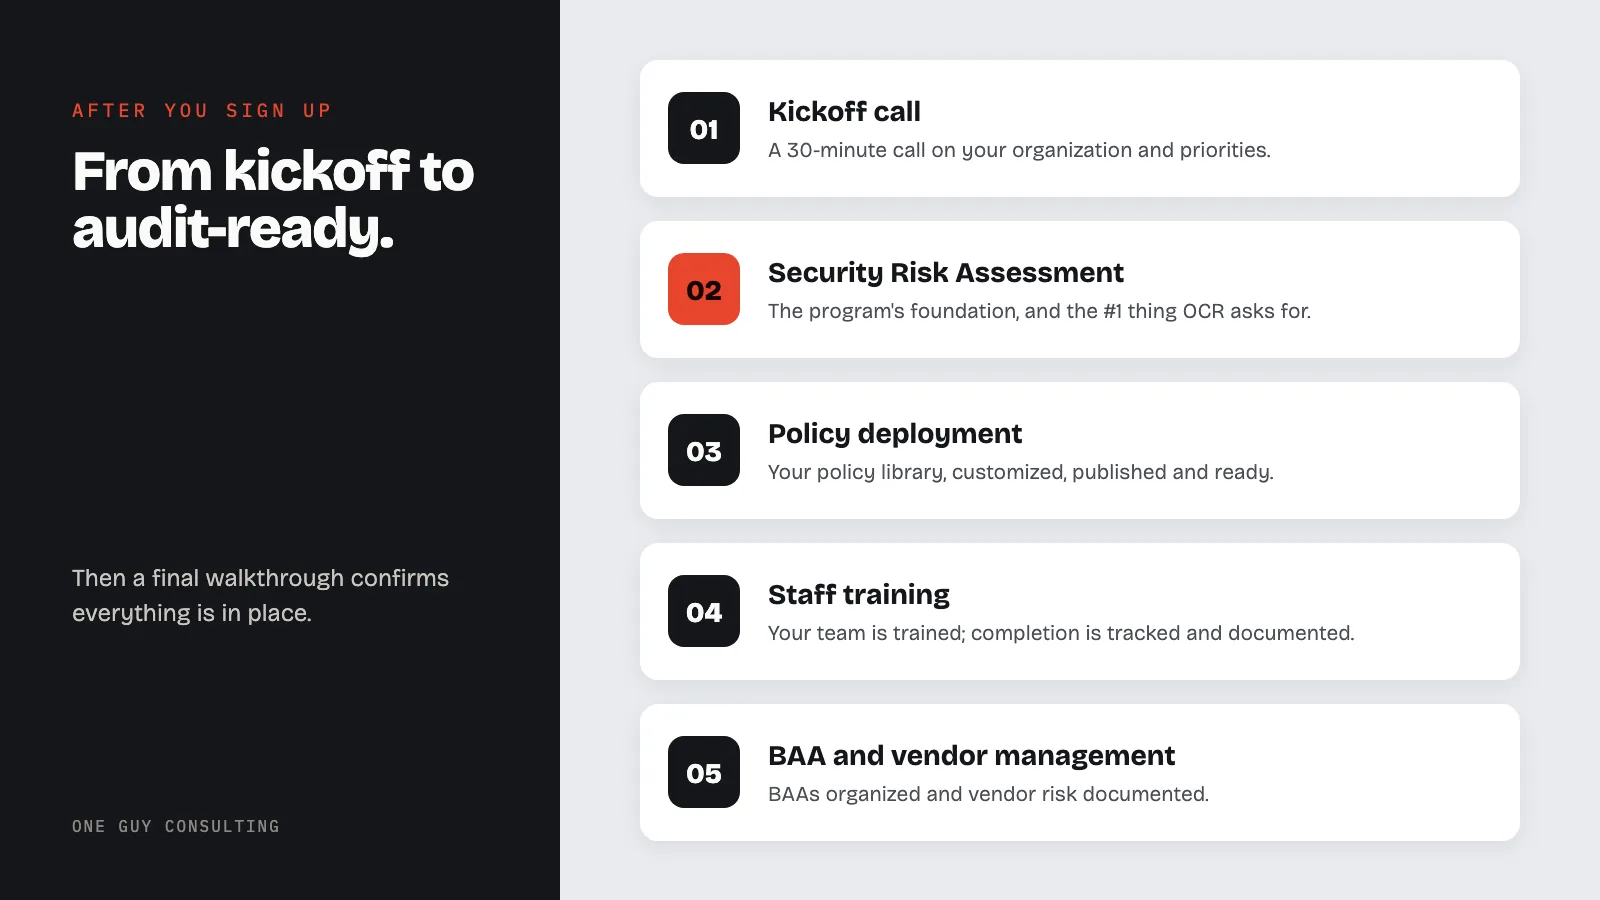
From kickoff to audit-ready
Kickoff Call
A focused 30-minute call to understand your organization, your current state, and your priorities.
- Identify your organization type (Covered Entity or Business Associate)
- Understand your current compliance posture
- Set timeline expectations and assign your Privacy Officer portal access
Security Risk Assessment
The foundation of your entire compliance program, and the #1 thing OCR asks for.
- Guided risk assessment through your portal, no spreadsheets or guesswork
- Identify threats, vulnerabilities, and current safeguards
- Generate your documented risk analysis (required by 45 CFR § 164.308)
Policy Deployment
Your full HIPAA policy library: customized, published, and ready for your workforce.
- Policies tailored to your organization's size, type, and operations
- Covers Privacy Rule, Security Rule, and Breach Notification
- Published to your branded compliance portal, accessible anytime
Staff Training
Your team gets trained, with completion tracked and documented for audit evidence.
- Role-based training modules assigned to each employee
- Completion tracking with attestation records
- Annual refresher reminders built in
BAA & Vendor Management
Get your Business Associate Agreements organized and your vendor risk documented.
- BAA generation and tracking through your portal
- Vendor inventory with risk categorization
- Due diligence documentation for each vendor relationship
Audit Readiness Review
A final walkthrough to confirm everything is in place: policies, training, risk assessment, BAAs.
- Compliance gap check against all HIPAA requirements
- Remediation plan for any remaining items
- Your organization is audit-ready
Continuous Compliance
Compliance isn't a one-time project. Your portal keeps you current, year after year.
- Annual risk assessment reminders and updates
- Training renewal tracking
- Incident management and breach notification tools
- Policy updates as regulations change
Typical timeline for small-to-mid-size organizations. Your timeline may vary based on organization size and complexity.
What We Promise
No Wasted Time
Guided process: we tell you exactly what's needed at each step
Full Picture
Privacy, Security, and Breach Notification Rules, all addressed in one program
Built for Humans
Policies written so your staff can actually read, understand, and follow them
Ready to get started?
Let's book your kickoff. Want more detail on each phase? Read the complete HIPAA compliance process.