HIPAA compliance for business associates.
Under the HITECH Act, a business associate answers to HIPAA on its own. We help BAs set up sound ways to handle PHI, keep watch over their vendors, and run BAAs that hold up.
Duties under 45 CFR 164.308 to 164.312, 164.410, and 164.502(e)
How we help business associates handle PHI
Under the HITECH Act and the Omnibus Rule, a business associate answers directly for the HIPAA Security Rule, and for parts of the Privacy Rule. So if you create, receive, maintain, or transmit PHI for a covered entity, the duties are yours too. They do not stop with the practice that hired you.
One Guy Consulting maps where PHI comes into your work, how it moves once it is there, and where the risk piles up. Then we build safeguards around those spots. You get real controls, not a stock checklist.
Key BA duties under HIPAA: Put administrative, physical, and technical safeguards in place (45 CFR 164.308 to 164.312). Tell the covered entity about a breach without unreasonable delay, and no later than 60 days (45 CFR 164.410). Get a signed BAA from any subcontractor that handles PHI (45 CFR 164.502(e)).45 CFR 164.410 · 45 CFR 164.502(e)
Managing your own subcontractors and vendors
If you are a business associate and your subcontractors can reach PHI, you owe the same watch over them that a covered entity owes you. That means a BAA with each one, notes on the checks you ran, and a running view of where each one stands.
We set up a way to manage vendors that grows with how many you have and how much risk they carry.
Vendor Inventory and Risk Tiering
List every vendor that touches PHI. Sort them into risk tiers by what they can reach, how much data they hold, and how deeply they tie into your systems.
Due Diligence Documentation
Set questions for each vendor, and one place to keep their answers, so you can show your work to a covered entity or an auditor.
Ongoing Compliance Monitoring
A set review cycle, renewal dates you can see, and a clear next step when a vendor slips.
For the full take on risk tiers and our five-step process, see HIPAA Vendor Management.
Business Associate Agreement lifecycle
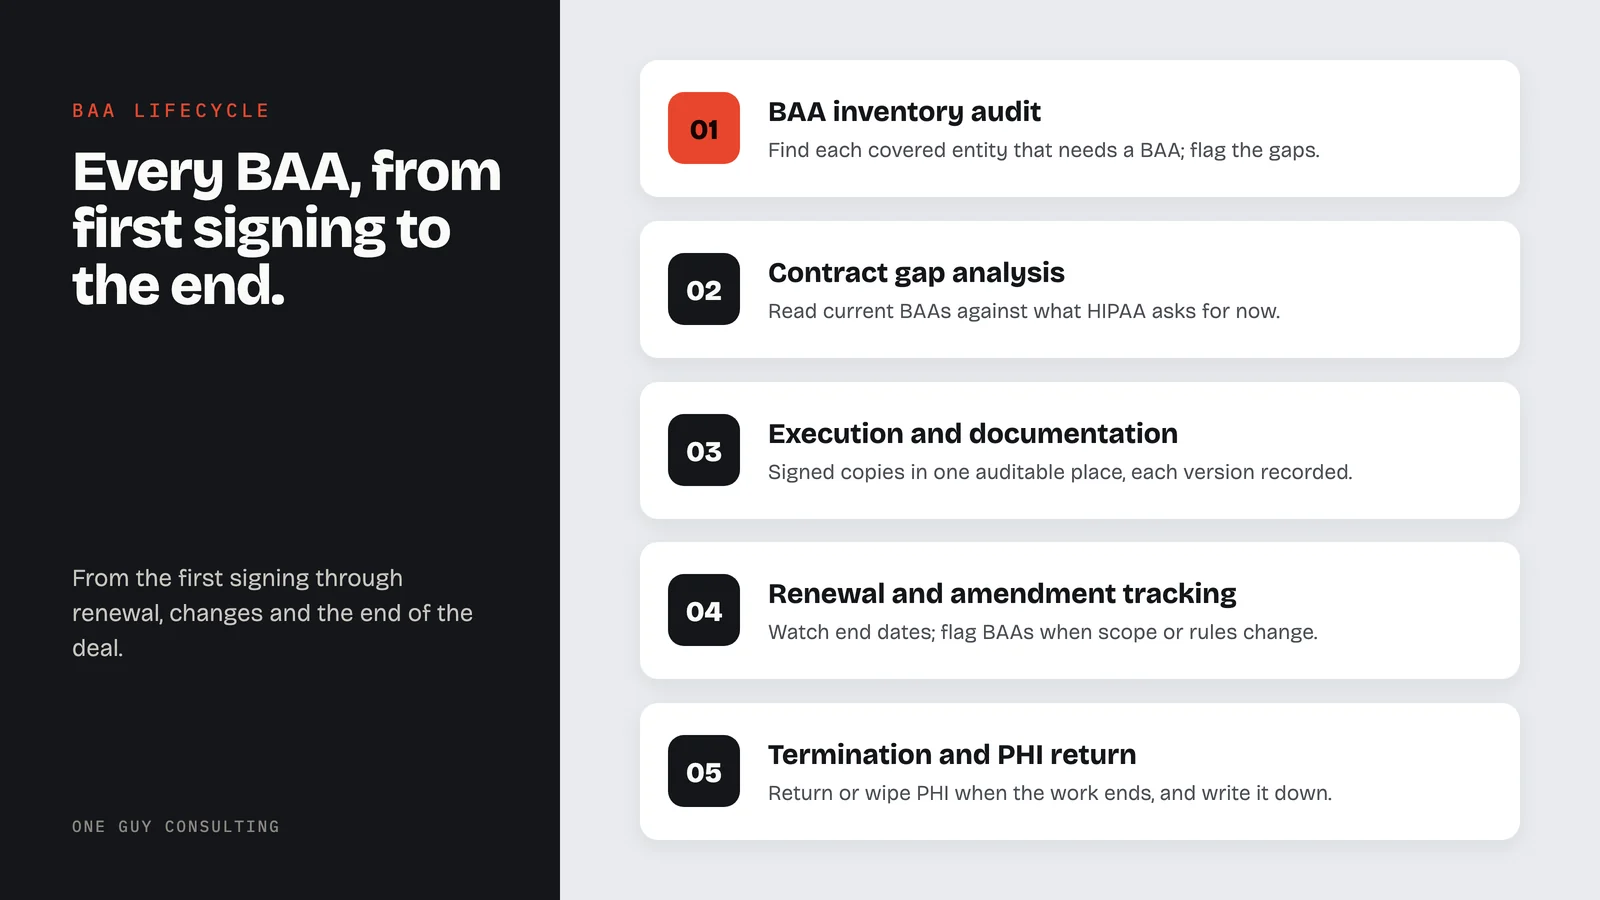
A BAA is not a box to tick. It sets out how PHI may be used and disclosed, what safeguards each side owes, and who answers for what. We help business associates handle BAAs from the first signing through renewal, changes, and the end of the deal.
- 01
BAA Inventory Audit
Find every covered entity you work with that needs a BAA. Flag the ones you never got, and the drafts no one signed.
- 02
Contract Review and Gap Analysis
Read the BAAs you already have against what HIPAA asks for now. Spot the clauses that take on more than you meant, and the ones that leave something out.
- 03
Execution and Documentation
Get them signed. Keep every signed copy in one place you can audit, with a record of each version.
- 04
Renewal and Amendment Tracking
Watch the end dates. Flag any BAA that needs work because the scope shifted, a new service came online, or the rules changed.
Scope, services, rules - 05
Termination and PHI Return
When the work ends, run the return or the wipe of PHI that HIPAA calls for, and write down that it was done.
For what the terms mean, what it costs, and how the portal works, see BAA Management Services.
Business Associate Agreements: key compliance facts
- What a BAA is. The written contract HIPAA requires between a covered entity and any vendor that creates, receives, maintains, or transmits PHI on its behalf.
- When it is required. Before any PHI changes hands. A signed BAA is a precondition, not a formality, per 45 CFR 164.308(b)(1) and 45 CFR 164.502(e).
- Required contents. The elements listed at 45 CFR 164.504(e): permitted uses and disclosures, required safeguards, breach and incident reporting, subcontractor flow-down, and return or destruction of PHI at termination.
- Who signs. Both the covered entity and the business associate. Subcontractors that touch PHI need their own BAAs with the business associate.
- Common gaps OCR cites. Missing BAAs, agreements that omit required elements, and no BAA with cloud or software vendors that store PHI.
An employee is workforce, not a business associate, and signs a confidentiality agreement rather than a BAA.
Common business associate types
IT and MSPs
Managed service providers, cloud hosts, and IT support firms that reach ePHI while they run your systems.
Billing and Revenue Cycle
Billing services, clearinghouses, and coding firms that work on claims that hold PHI.
EHR and SaaS Vendors
Software firms that store, handle, or send PHI as part of what they sell to a covered entity.
Shredding and Disposal
Shredding firms and media wipe services that get rid of PHI on paper or on a drive.
Legal and Accounting
Law firms, CPAs, and consultants who see PHI while they do work for a covered entity.
Answering Services
After-hours call centers and patient messaging tools that take in or pass along PHI for a practice.
For the full picture on BA consulting, see HIPAA for Business Associates.
Two plans for business associates.
Two plans, six ways to pay. No per-user fees. Pick the level of help you want from Chuck.
- The platform on its own
- SRA, gap analysis, remediation plans
- Policy templates and staff training
- Vendor and BAA management
- Everything in Self-Guided
- 4 hours a month of 1:1 implementation calls with Chuck
- Incident response guidance
- CMS audit response support
One payment, two full years of coverage.
Secure checkout by Stripe. Your payment details go straight to Stripe and never touch our servers.
Business associate compliance questions
Is a business associate independently liable under HIPAA?+
Do business associates need their own risk assessment?+
What happens if a BA uses subcontractors who access PHI?+
How quickly must a BA report a breach?+
Need help with business associate compliance?
Book a short call. We will tell you where you stand and what to fix first.
Questions about BA compliance?
Or email us at hello@oneguyconsulting.com · Book your free 30-minute intro call