HIPAA Status Tune-Up
A HIPAA compliance self-assessment evaluates whether your practice meets the administrative, physical, and technical safeguard requirements of the HIPAA Security Rule (45 CFR 164.308) and the Privacy Rule (45 CFR Part 164). This assessment evaluates your practice's alignment with federal HIPAA requirements across 10 key compliance areas. Results are confidential and delivered by email.
What This Assessment Covers
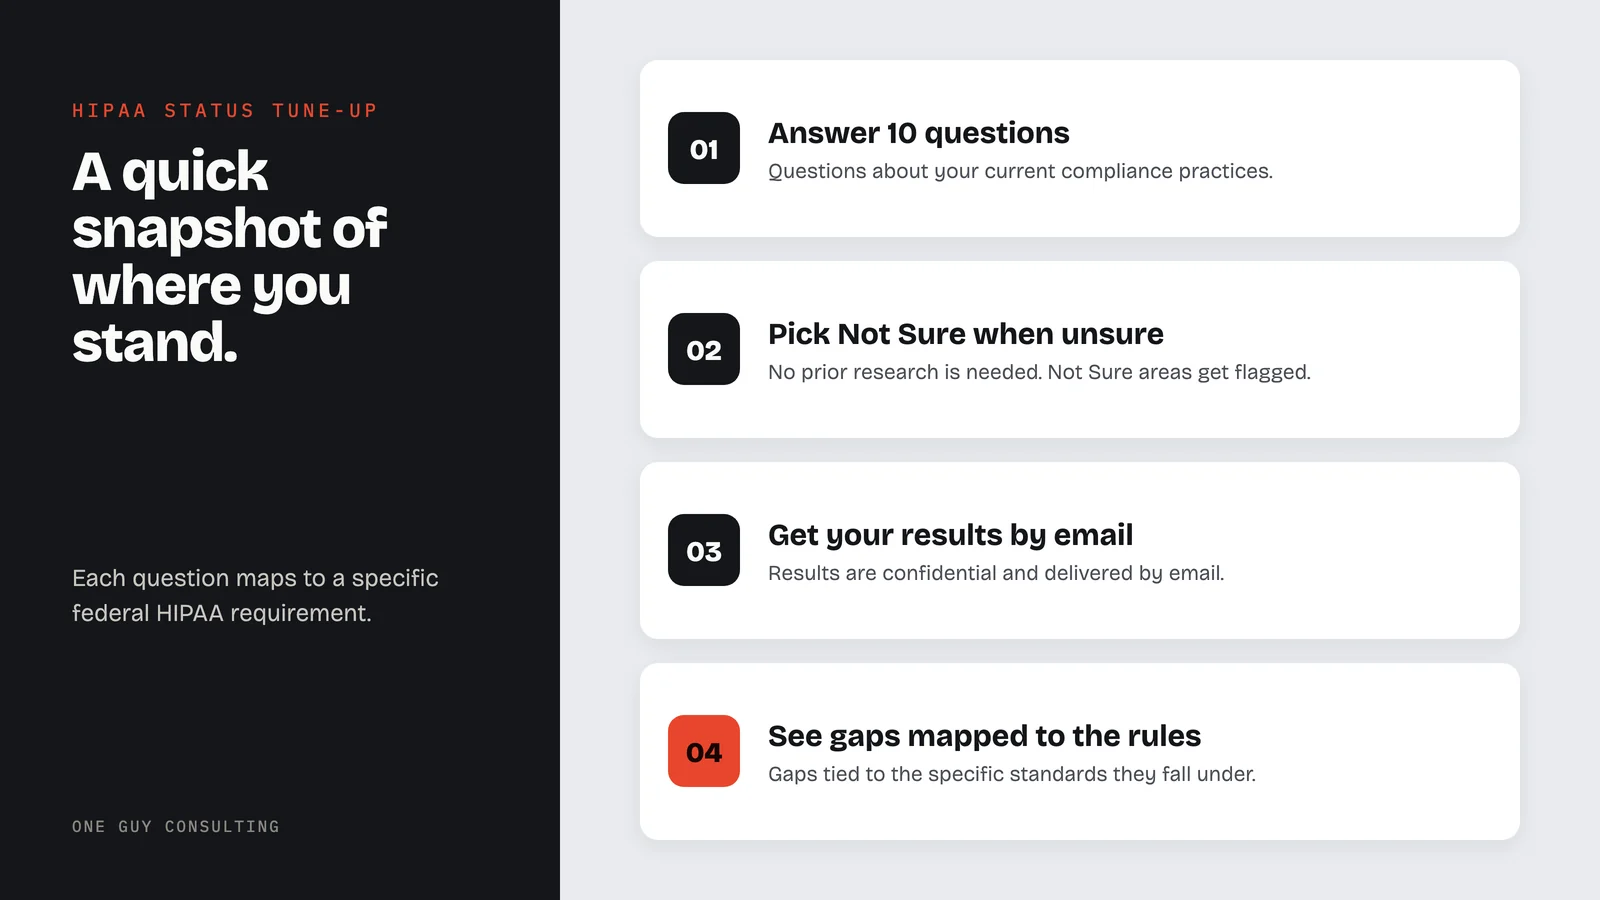
Each question in this assessment maps to a specific federal HIPAA requirement. The five primary compliance areas evaluated are:
- Risk Analysis45 CFR 164.308(a)(1)
- Workforce Training45 CFR 164.308(a)(5)
- Business Associate Agreements45 CFR 164.308(b)
- Access Controls45 CFR 164.312(a)
- Incident Response45 CFR 164.308(a)(6)
How It Works
Answer 10 questions about your current compliance practices.
No prior research is needed. Select "Not Sure" for any area you cannot confirm.
Results are confidential and delivered by email. The assessment takes approximately 2 minutes.
Evaluate your HIPAA compliance readiness
This assessment covers risk analysis (45 CFR 164.308(a)(1)), workforce training (164.308(a)(5)), business associate agreements (164.308(b)), access controls (164.312(a)), and incident response (164.308(a)(6)). Answer 10 questions. No prior research is needed. Results are confidential and delivered by email.
See your status tune-up results in mere moments.
Just enter your email and we will send your confidential results.
Check your inbox!
Your confidential HIPAA status tune-up results are on the way. Keep an eye out for an email from One Guy Consulting.
Book Your Free 30-Minute Intro CallWant to talk through your results? Schedule a free 15-minute call.
The 10 Questions at a Glance
The assessment asks whether your organization has the following safeguards in place:
- Annual Security Risk Assessment164.308(a)(1)(ii)(A)
- Gap Report derived from risk assessment findings164.308(a)(1)(ii)(B)
- Remediation Plans built from gap report findings164.308(a)(1)(ii)(B)
- Documentation reflecting 2025 Privacy Rule amendments45 CFR Part 164, Subpart E
- Inventory of all devices that can access PHI164.310(d)
- Annual workforce training including policy attestation and cybersecurity awareness164.308(a)(5)
- Unique login credentials for each staff member accessing PHI systems164.312(a)(2)(i)
- Business Associate Agreements with all required third parties164.308(b)(1)
- Security vetting of prospective business associates164.314(a)
- Anonymous reporting mechanism for unauthorized PHI disclosures164.308(a)(6)
Why Self-Assessment Matters
The HIPAA Security Rule requires covered entities to conduct periodic evaluations of their security measures (45 CFR 164.308(a)(8)). A self-assessment provides an initial benchmark of compliance readiness before a formal Security Risk Assessment. Organizations that identify gaps early can prioritize remediation and reduce the risk of enforcement action.
This content is for educational and informational purposes only and should not be construed as legal advice.
HIPAA Status Tune-Up FAQ
Everything you need to know about this assessment.
The questions in this assessment map directly to the administrative safeguard requirements of the HIPAA Security Rule (45 CFR §164.306), the physical and technical safeguard standards, and the Privacy Rule's workforce training and accountability provisions. The answers you provide help identify which regulatory areas may require attention before your next compliance review or HHS audit.
What does this status tune-up cover?+
The status tune-up asks about the major areas of HIPAA compliance including policies, training, risk assessments, breach procedures, and business associate management. It is designed to give you a quick snapshot, not a full audit. Specifically, the questions align with the administrative safeguards at 45 CFR §164.308, which cover risk analysis (§164.308(a)(1)), workforce training (§164.308(a)(5)), and business associate contracts (§164.308(b)), as well as the general security standards framework at 45 CFR §164.306.
Is this actually free?+
Yes, completely free with no strings attached. We send you a personalized results report and that is it. No surprise sales calls unless you book a consultation yourself.
How long does it take?+
About 2 minutes. There are no trick questions and you do not need to look anything up. If you are not sure about an answer, just pick "Not Sure" and we will flag that area in your report. "Not Sure" responses are meaningful: under HHS guidance on risk analysis, an organization's inability to confirm whether a safeguard is in place is itself an indicator of potential risk under §164.308(a)(1)(ii)(A).
Are my answers confidential?+
Absolutely. Your responses are sent directly to our secure system and your results email goes only to the address you provide. We do not share your information with anyone.
What happens after I get my results?+
You will receive an email with your scored results and suggested next steps. If you want to discuss your results with a compliance specialist, you can book a free 15-minute call from the results page or from the email itself. The results report maps any identified gaps to the specific regulatory standards they fall under, such as the risk management implementation specification at 45 CFR §164.308(a)(1)(ii)(B) or the workforce training standard at §164.308(a)(5), so you know exactly which requirements to prioritize.