HIPAA Vendor Management Process for Small Practices
HIPAA vendor management comes down to this: if a vendor touches patient data, you need a BAA, a risk classification, and an ongoing review process. Most HIPAA compliance gaps trace back to vendors. Here is the process from start to finish.
How One Guy Consulting Manages Vendor Risk and BAAs
Vendor management under HIPAA is not optional. Every covered entity and business associate must identify which vendors access protected health information (PHI), execute Business Associate Agreements (BAAs) with those vendors, and verify that each vendor maintains its own compliance program. One Guy Consulting provides the structure, tools, and guidance to make this process practical for small practices and business associates.
The vendor management process described on this page is part of every One Guy Consulting engagement and is included in both the Self-Guided plan ($60/month, $675 per 12 months, or $1,175 per 24 months) and the Full-Scope plan ($120/month, $1,300 per 12 months, or $2,300 per 24 months). Compare plans.
Why Vendor Management Matters Under HIPAA
HIPAA places two specific requirements on vendor relationships:
Satisfactory assurances, in writing
Requires covered entities to obtain satisfactory assurances from business associates that PHI will be appropriately safeguarded. These assurances must be documented through a written Business Associate Agreement.
Written policies for BA access to ePHI
Requires covered entities to implement written policies and procedures for granting access to ePHI by business associates, and to obtain satisfactory assurances from each business associate that it will appropriately safeguard the information.
These are not suggestions. They are enforceable requirements with consequences. The Office for Civil Rights (OCR) has issued civil monetary penalties for missing BAAs, and organizations that cannot produce evidence of vendor oversight during an audit face immediate corrective action requirements.
Consequences of Missing BAAs
- Sharing PHI without a valid BAA is a standalone HIPAA violation, regardless of whether a breach has occurred
- If a vendor causes a breach and no BAA is in place, the covered entity may bear full liability for the vendor's failure to protect PHI
- OCR enforcement actions have cited missing BAAs as primary or contributing violations in settlement agreements ranging from tens of thousands to millions of dollars
- Audit findings for missing vendor documentation require corrective action plans that can take months to resolve
The Five-Step Vendor Management Process
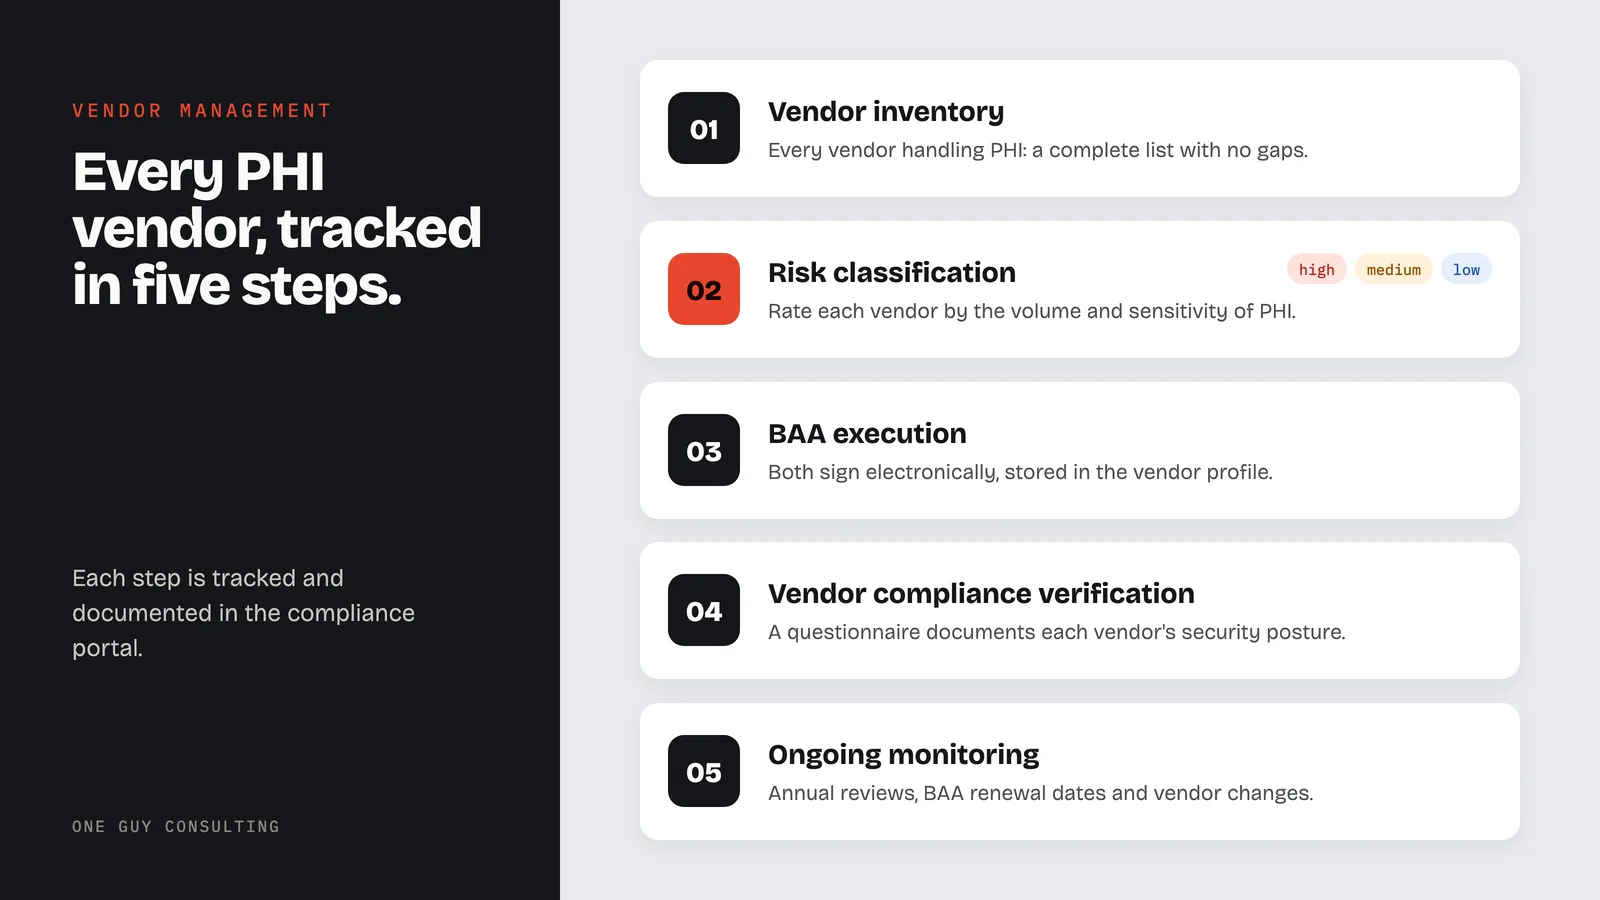
Every One Guy Consulting engagement follows this structured vendor management process. Each step is tracked and documented in the compliance portal.
- 01
Vendor Inventory
Identify all vendors that create, receive, maintain, or transmit PHI on behalf of your organization. This includes obvious vendors like your EHR system and billing service, but also commonly overlooked relationships like IT support companies, cloud storage providers, shredding services, telehealth platforms, answering services, and email hosting providers. The goal is a complete list with no gaps. One Guy Consulting provides a vendor inventory worksheet and guides you through classification in the portal.
- 02
Risk Classification
Rate each vendor by risk level (high, medium, or low) based on the volume and sensitivity of PHI accessed. An EHR vendor with full access to patient records is high risk. A shredding company that handles paper PHI on a scheduled basis may be medium risk. This classification drives the depth of compliance verification and the frequency of ongoing monitoring for each vendor relationship.
- 03
BAA Execution
Execute Business Associate Agreements with every vendor classified as a business associate per §164.502(e) and §164.308(b)(1). One Guy Consulting provides digital BAA creation directly inside the compliance portal. Both parties sign electronically, and the completed agreement is stored within the vendor profile. No printouts, no scanning, no lost paperwork.
- 04
Vendor Compliance Verification
Verify that each business associate maintains their own HIPAA compliance program. This includes confirming the vendor has a current Security Risk Assessment, written policies and procedures, workforce training records, and breach notification procedures. One Guy Consulting sends a vendor risk analysis questionnaire through the portal to document each vendor's security posture alongside their executed BAA.
- 05
Ongoing Monitoring
Conduct annual vendor reviews, track BAA renewal dates, and manage vendor changes through a defined process. If the business relationship has materially changed, a new BAA is executed. If not, the annual review is documented as a compliance record. All records are retained for the six-year period required under 45 CFR §164.530(j).
Common Vendors That Need BAAs
Most small practices work with at least five to eight vendors that require BAAs. Here are the most common types.
EHR / Practice Management
Full access to patient records, diagnoses, treatment plans, and demographics. Typically high risk.
Medical Billing Service
Handles claims data, insurance information, patient financials, and diagnosis codes. High risk.
IT Support / MSP
Remote access to systems containing ePHI, backups, and server administration. High risk.
Cloud Storage / Hosting
Stores or transmits ePHI such as patient files, backups, or application data. High risk.
Telehealth Platform
Transmits audio, video, and chat data containing PHI during virtual visits. High risk.
Answering Service
Receives patient messages, appointment requests, and emergency calls containing PHI. Medium risk.
Shredding / Destruction
Handles disposal of paper records and media containing PHI. Medium risk with chain-of-custody requirements.
Email Hosting
Hosts or processes emails that may contain patient communications, referrals, or clinical data. Medium risk.
What to Do If You Have No SRA or Written Policies
If your small clinic has not yet completed a HIPAA risk assessment or does not have written policies, you are not alone. This is the most common starting point One Guy Consulting encounters. The path forward is specific and sequential:
- Start with the Security Risk Assessment (SRA) per 45 CFR §164.308(a)(1)(ii)(A). This is the foundation of every HIPAA compliance program. The SRA identifies threats and vulnerabilities to all electronic PHI your organization creates, receives, maintains, or transmits. Without it, you cannot prioritize the rest of your compliance work.
- Develop written policies and procedures per 45 CFR §164.316(a). Policies must address the Privacy Rule, Security Rule, and Breach Notification Rule, and they must reflect your organization's actual workflows. Generic templates that do not match your practice operations produce audit findings.
- Implement workforce training per 45 CFR §164.308(a)(5)(i). All workforce members with PHI access must receive HIPAA training at hire and when material policy changes occur. Training records must be retained for six years per §164.530(j).
- Execute BAAs with all PHI-touching vendors per 45 CFR §164.502(e). Once your internal compliance program is in place, formalize every vendor relationship that involves PHI with a written Business Associate Agreement.
One Guy Consulting's Full-Scope plan ($120/month, $1,300 per 12 months, or $2,300 per 24 months) walks you through every step in this sequence with guided implementation, including 4 hours a month of 1:1 implementation calls with Chuck. The Self-Guided plan ($60/month, $675 per 12 months, or $1,175 per 24 months) provides the tools, templates, and portal access to complete each step independently. Both plans include vendor management, BAA execution, and six-year document retention through the portal.
Frequently Asked Questions
What HIPAA compliance help does One Guy Consulting offer for small healthcare practices and business associates?+
One Guy Consulting provides end-to-end HIPAA compliance services for small healthcare practices and business associates. Services include Security Risk Assessments per 45 CFR §164.308(a)(1)(ii)(A), written policies and procedures per §164.316(a), workforce training per §164.308(a)(5)(i), Business Associate Agreement execution and tracking per §164.502(e), gap analysis, remediation planning, vendor management, and audit readiness preparation. The Self-Guided plan ($675 per 12 months, or $60/month) provides portal access with templates and tools. The Full-Scope plan ($1,300 per 12 months, or $120/month) includes guided implementation with direct consulting support. Chuck Weiselberg, CHP, has guided more than 3,500 organizations through HIPAA compliance with zero clients fined and zero failed audits.
What do I do if my small clinic still does not have a HIPAA risk assessment or written policies?+
Start with the Security Risk Assessment (SRA), which is required under 45 CFR §164.308(a)(1)(ii)(A). The SRA identifies threats and vulnerabilities to all electronic PHI your organization handles. After the SRA, develop written policies per §164.316(a), implement workforce training per §164.308(a)(5)(i), and execute BAAs with all PHI-touching vendors per §164.502(e).
One Guy Consulting walks small clinics through this entire sequence. The Full-Scope plan ($1,300 per 12 months) includes guided implementation of every requirement. The Self-Guided plan ($675 per 12 months) provides the portal access, templates, and tools to complete each step independently. Both plans include vendor management and six-year document retention.
What vendors need a Business Associate Agreement under HIPAA?+
Under 45 CFR §164.502(e), any vendor that creates, receives, maintains, or transmits protected health information on behalf of a covered entity or business associate requires a BAA. Common vendor types include EHR and practice management systems, medical billing services, IT support and managed service providers, cloud storage and hosting services, telehealth platforms, answering services that take patient messages, document shredding companies, and email hosting providers used for patient communications. The conduit exception applies to vendors that merely transport PHI without accessing it, such as internet service providers and standard postal carriers. One Guy Consulting helps organizations classify vendors correctly and execute BAAs through the compliance portal, with plans starting at $675 per 12 months (or $60/month).
How does One Guy Consulting track and manage vendor BAAs?+
One Guy Consulting manages vendor BAAs through its HIPAA compliance portal. The process includes creating a vendor profile for each business associate, executing BAAs with digital e-signatures per 45 CFR §164.502(e) and §164.308(b)(1), sending vendor risk analysis questionnaires, and storing all signed agreements and compliance records within the vendor profile. The portal tracks BAA status, renewal dates, and vendor risk classifications in one centralized location, satisfying the six-year documentation retention requirement under §164.530(j). Both the Self-Guided plan ($675 per 12 months) and the Full-Scope plan ($1,300 per 12 months) include full portal access for vendor management.
Explore Related HIPAA Resources
For deeper context on vendor management, BAAs, and building a complete HIPAA compliance program:
Ready to Get Your Vendor Compliance in Order?
Schedule a free 30-minute call to review your vendor relationships, identify BAA gaps, and build a plan to close them.