For a health care provider, HIPAA has no small-business exemption. Any provider that transmits health information electronically in a covered transaction is a covered entity (45 CFR 160.103) with the same duties as a large one, sized to the practice: a risk analysis, written policies, trained staff, BAAs, privacy and security officials, and six years of records.
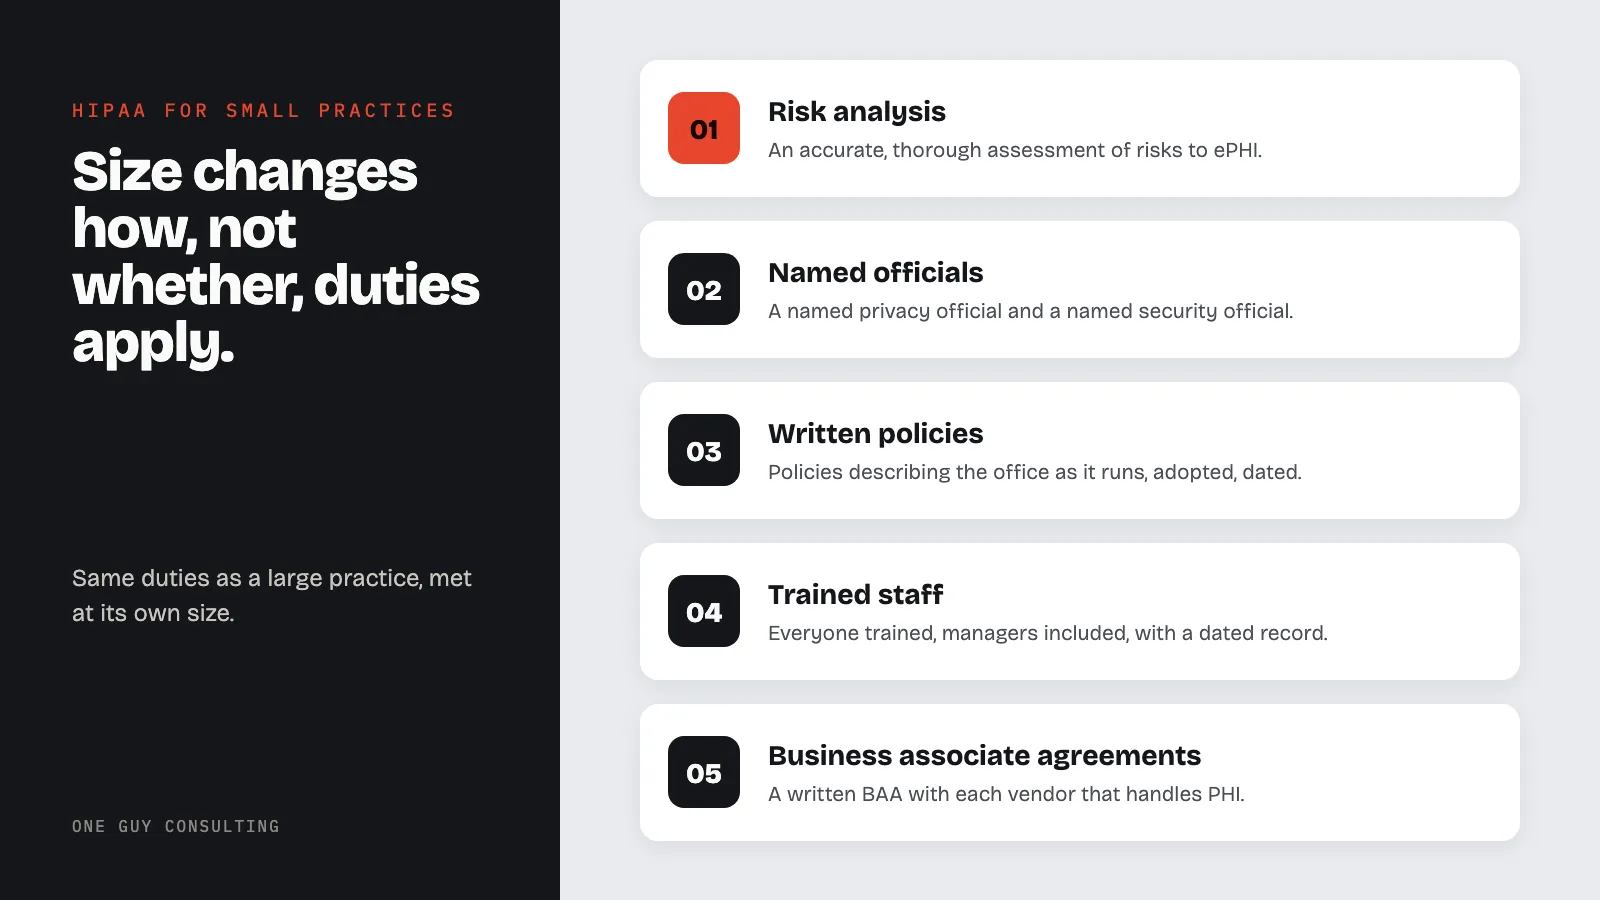
That is HIPAA compliance for small business in health care (45 CFR 164.306(b), 164.530(i)).
The question can arrive from outside. A billing company sends a business associate agreement to sign. A new hire asks where the HIPAA policies are kept. The owner or office manager of a 2 to 5 person practice then needs to know what the rule asks of an office this size.
This guide answers from the regulation text: each duty with its section, what scales, policies, training, and what help costs.
HIPAA Compliance for Small Business: What a Small Practice Must Have
The Privacy Rule, the Security Rule and the Breach Notification Rule reach a three-person practice through the same sections that reach a hospital. Size changes how each duty is met, not whether it applies.
Whether HIPAA Applies to Your Practice
The test is in the definitions. Under 45 CFR 160.103, a covered entity includes "A health care provider who transmits any health information in electronic form in connection with a transaction covered by this subchapter." For small medical practices, the test has no headcount, revenue or patient-volume threshold.
The transactions listed in 160.103 open with "Health care claims or equivalent encounter information." A practice that bills insurers electronically fits that list. Whether a particular practice meets the definition, such as one that takes no insurance, is a question for a healthcare attorney. A one-person office has its own wrinkles, covered in HIPAA compliance for solo practitioners.
The Duties, One by One
Nine of the duties in the rules, each with its section and its own words. The right-hand column is an illustration, not a legal standard.
| Duty | Section | The rule's words | In a 3-person office |
|---|---|---|---|
| Risk analysis | 45 CFR 164.308(a)(1)(ii)(A) | "Conduct an accurate and thorough assessment of the potential risks and vulnerabilities to the confidentiality, integrity, and availability of electronic protected health information" | A written assessment of the EHR, email, front desk computer, phones and backups. |
| Security official | 45 CFR 164.308(a)(2) | "Identify the security official who is responsible for the development and implementation of the policies and procedures required by this subpart" | One named person, in writing, dated. |
| Privacy official and complaint contact | 45 CFR 164.530(a)(1)(i) and (ii) | "A covered entity must designate a privacy official who is responsible for the development and implementation of the policies and procedures of the entity." | A named privacy official and a named contact for patient complaints. |
| Written policies | 45 CFR 164.316(a) and 164.530(i)(1) | "Implement reasonable and appropriate policies and procedures to comply with the standards, implementation specifications, or other requirements of this subpart" | Policies that describe the office as it runs, adopted and dated. |
| Training | 45 CFR 164.308(a)(5)(i) and 164.530(b) | "Implement a security awareness and training program for all members of its workforce (including management)." | Everyone trained, managers included, with a dated record. |
| Business associate agreements | 45 CFR 164.308(b)(1) | "only if the covered entity obtains satisfactory assurances" | A written BAA with each vendor that handles PHI for the office, such as a billing service. |
| Notice of Privacy Practices | 45 CFR 164.520(c)(2)(iii)(B) and (c)(3)(i) | "Post the notice in a clear and prominent location where it is reasonable to expect individuals seeking service from the covered health care provider to be able to read the notice" (at a physical service delivery site); a practice with a web site that "provides information about the covered entity's customer services or benefits must prominently post its notice on the web site" | A copy at the first visit, a good faith attempt at a signed acknowledgment, a copy on the waiting room wall and one on the practice web site. |
| Breach notification | 45 CFR 164.404(b) | "without unreasonable delay and in no case later than 60 calendar days after discovery of a breach" | A written procedure naming who decides and who sends the letters. |
| Records | 45 CFR 164.316(b)(2)(i) and 164.530(j)(2) | "for 6 years from the date of its creation or the date when it last was in effect, whichever is later" | One file, paper or digital, with every policy version, training record, assessment and BAA. |
The risk analysis sits at the top for a reason. The next implementation specification, 45 CFR 164.308(a)(1)(ii)(B), says to "Implement security measures sufficient to reduce risks and vulnerabilities to a reasonable and appropriate level to comply with § 164.306(a)." A practice cannot size its measures to risks it has never written down. A practice starting from nothing can begin with what to do first when a clinic has no HIPAA program, then work the same duties as steps in the HIPAA compliance checklist for small practices.
What Scales With Size, and What Does Not
The Security Rule builds size into its text. 45 CFR 164.306(b)(1) says covered entities "may use any security measures that allow the covered entity or business associate to reasonably and appropriately implement the standards and implementation specifications as specified in this subpart." Under 164.306(b)(2)(i) to (iv), that choice weighs four factors: size, complexity and capabilities; technical infrastructure; the costs of security measures; and the probability and criticality of risks.
Policies carry the same factors. 45 CFR 164.316(a) calls for policies "taking into account those factors specified in § 164.306(b)(2)(i), (ii), (iii), and (iv)." On the Privacy Rule side, 164.530(i)(1) says "The policies and procedures must be reasonably designed, taking into account the size and the type of activities that relate to protected health information undertaken by a covered entity, to ensure such compliance."
- Scales: which security tools the office buys, how long each policy runs, and the training format (the text sets none).
- Does not scale: meeting each applicable Security Rule standard (164.306(c)), a named privacy official and a named security official, the risk analysis, training for every workforce member, a BAA with each business associate, the 60-day outer limit for breach notice, and six years of records.
Small providers are not left out of enforcement listings. The HHS Office for Civil Rights resolution agreements page lists Small Health Care Provider Fails to Implement Multiple HIPAA Security Rule Requirements (July 23, 2020). A neurology practice appears there too: HHS Office for Civil Rights Settles HIPAA Ransomware Cybersecurity Investigation with Neurology Practice (April 25, 2025).
Policies That Fit How Your Office Works
HIPAA policies do not have to start from a blank page. The sections above ask for policies that are reasonable, appropriate and designed around the practice's size and activities; they do not say who writes the first draft. A policy and procedure template gives the structure. The practice makes each policy describe the office that exists, then adopts it.
A template that was never fitted to the office shows it:
- It refers to an IT department the practice does not have.
- Its incident procedure runs through titles nobody in the office holds.
- Its breach procedure never names who sends the notices.
45 CFR 164.316(b)(2)(iii) says to "Review documentation periodically, and update as needed, in response to environmental or operational changes affecting the security of the electronic protected health information." Under 164.316(a), a practice "may change its policies and procedures at any time, provided that the changes are documented and are implemented in accordance with this subpart." The text does not prescribe a format. A version date, the approver's name and a record of each review are one way to show both.
Both One Guy Consulting plans include policy and procedure templates, which the practice fills in with its own people, systems and procedures and adopts. The HIPAA policy templates page shows what the library covers.
Training a Small Team, and the Records That Prove It
HIPAA training for small businesses in health care comes from two sections. 45 CFR 164.530(b)(1) says "A covered entity must train all members of its workforce on the policies and procedures with respect to protected health information required by this subpart and subpart D of this part, as necessary and appropriate for the members of the workforce to carry out their functions within the covered entity." The Security Rule, at 164.308(a)(5)(i), adds "(including management)", so managers are trained too.
The Privacy Rule sets training timing by events, not the calendar. Under 164.530(b)(2)(i)(B), a new workforce member is trained "within a reasonable period of time after the person joins the covered entity's workforce". Under 164.530(b)(2)(i)(C), staff affected by a material change in policies or procedures are trained "within a reasonable period of time after the material change becomes effective". The Security Rule's training standard adds "Periodic security updates" as an addressable implementation specification (164.308(a)(5)(ii)(A)) and sets no interval. Neither 164.530 nor 164.308 uses the word annual. A yearly refresher is a schedule a practice may choose, not a line in the regulation.
45 CFR 164.530(b)(2)(ii) says "A covered entity must document that the training as described in paragraph (b)(2)(i) of this section has been provided". The text does not list what the record must contain. A practical record shows:
- The date, matched to a policy version or the event that triggered it.
- The topics, tied to the practice's own policies.
- Who delivered it, and each attendee's signature or completion record.
- The materials: slides, handout, quiz or module.
45 CFR 164.530(j)(2) requires that documentation be kept "for six years from the date of its creation or the date when it last was in effect, whichever is later."
Who Does What, and What Help Costs
The practice owns its compliance. The officials it names make the decisions, adopt the policies and sign the agreements. Outside help can supply software, templates and structure; the duties stay with the covered entity.
One Guy Consulting offers two plans. Self-Guided is the compliance software: a Security Risk Assessment tool, automated gap analysis and remediation plans, policy and procedure templates, staff training and progress tracking, administrative, physical and technical audits, vendor management with digital BAAs, incident management and a compliance dashboard. Full-Scope includes everything in Self-Guided plus 4 hours a month of 1:1 implementation calls with Chuck to get your plan set up, personalized implementation, incident response guidance, and CMS audit response support, which also covers an OCR letter or investigation.
On those calls, Chuck Weiselberg, C.H.P., a consultant since 2015, walks the practice through the software and the process. He guides you through answering the audit (the Security Risk Assessment), guides training delivery, and gives incident response guidance as needed. The practice makes every decision. One Guy Consulting is not a law firm, so legal questions go to a healthcare attorney. All work is remote.
| Payment timeline | Self-Guided | Full-Scope |
|---|---|---|
| Monthly | $60 a month | $120 a month |
| 12 months, paid upfront | $675 | $1,300 |
| 24 months (loyalty pricing) | $1,175 | $2,300 |
There are no per-user fees: a 5-person office pays the same as a 25-person office on the same plan. Typical setup for a small practice takes weeks, not months. For what other kinds of help cost, see how much HIPAA consulting costs a small practice.
This article is educational and is not legal advice. For how the law applies to a specific practice, speak with a healthcare attorney.
FAQ
Does HIPAA apply to small businesses?
Yes, when the business is a covered entity or a business associate. HIPAA compliance for small business turns on the definitions in 45 CFR 160.103. For a health care provider, headcount is not part of the test: a provider that transmits health information electronically in connection with a covered transaction, such as an insurance claim, is a covered entity at any size. Whether a particular business meets a definition is a question for a healthcare attorney.
What are the HIPAA requirements for a small medical practice?
The same duties as a large practice, sized to the office. Among them: a risk analysis, a named security official and privacy official, written policies, workforce training, BAAs with each business associate, a Notice of Privacy Practices, a breach notification procedure and six years of records.
How often does HIPAA require workforce training?
The Privacy Rule sets triggers, not a calendar. Under 45 CFR 164.530(b)(2)(i), each new workforce member is trained "within a reasonable period of time after the person joins the covered entity's workforce", and staff affected by a material change in policies or procedures are trained after that change. The Security Rule adds "Periodic security updates" as an addressable implementation specification (164.308(a)(5)(ii)(A)) and sets no interval. Neither 164.530 nor 164.308 uses the word annual. A yearly refresher is a schedule a practice may choose.
Does a small practice need custom HIPAA policies, or can it use templates?
Templates can be the starting point. Under 45 CFR 164.530(i)(1), the policies "must be reasonably designed, taking into account the size and the type of activities that relate to protected health information undertaken by a covered entity". A template becomes the practice's policy once it names the practice's own people, systems and procedures and the practice adopts it.
Where can a small clinic get help with HIPAA compliance?
From the regulation text itself, a compliance software platform, or a consultant working alongside the software. One Guy Consulting's Full-Scope plan pairs the software with 4 hours a month of 1:1 implementation calls with Chuck Weiselberg, C.H.P., to get your plan set up, at $120 a month, $1,300 for 12 months or $2,300 for 24 months. Legal questions go to a healthcare attorney.
A small practice owes the same HIPAA duties as a large one, and the text lets it meet them at its own size. The work includes a risk analysis, a named privacy official and a named security official, adopted policies, trained staff, written BAAs and a records file kept for six years. The risk analysis comes first, because the Security Rule sizes security measures to the risks it finds (164.308(a)(1)(ii)(B)).
Want help putting this in place? The Full-Scope plan from One Guy Consulting pairs the compliance software with 4 hours a month of 1:1 implementation calls with Chuck Weiselberg, C.H.P., to get your plan set up. It is $120 a month, $1,300 for 12 months paid upfront, or $2,300 for 24 months, with no per-user fees. See how it works or book a free HIPAA compliance review. No obligation, no pressure.
Sources
- 45 CFR 160.103 (definitions: covered entity, transaction)
- 45 CFR 164.306 (Security Rule general rules and flexibility of approach)
- 45 CFR 164.308 (administrative safeguards)
- 45 CFR 164.316 (policies, procedures and documentation)
- 45 CFR 164.404 (notification to individuals)
- 45 CFR 164.520 (notice of privacy practices)
- 45 CFR 164.530 (Privacy Rule administrative requirements)
- HHS Office for Civil Rights, Resolution Agreements and Civil Money Penalties
Related Reading