HIPAA Staff Training Requirements for Small Practices
Frequency, Topics, Delivery Methods, and Attestation Explained
HIPAA says every team member must be trained. Here is what the rules say, what training must cover, and how we deliver it for practices with 1 to 20 staff.
What HIPAA Says About Workforce Training
The HIPAA Security Rule at 45 CFR 164.308(a)(5)(i) requires covered entities and business associates to "implement a security awareness and training program for all members of its workforce (including management)."
The HIPAA Privacy Rule at 45 CFR 164.530(b)(1) requires training on your organization's privacy policies and procedures for "each new member of the workforce within a reasonable period of time after the person joins" and whenever there are "material changes" to those policies.
HIPAA Training Frequency and Cadence
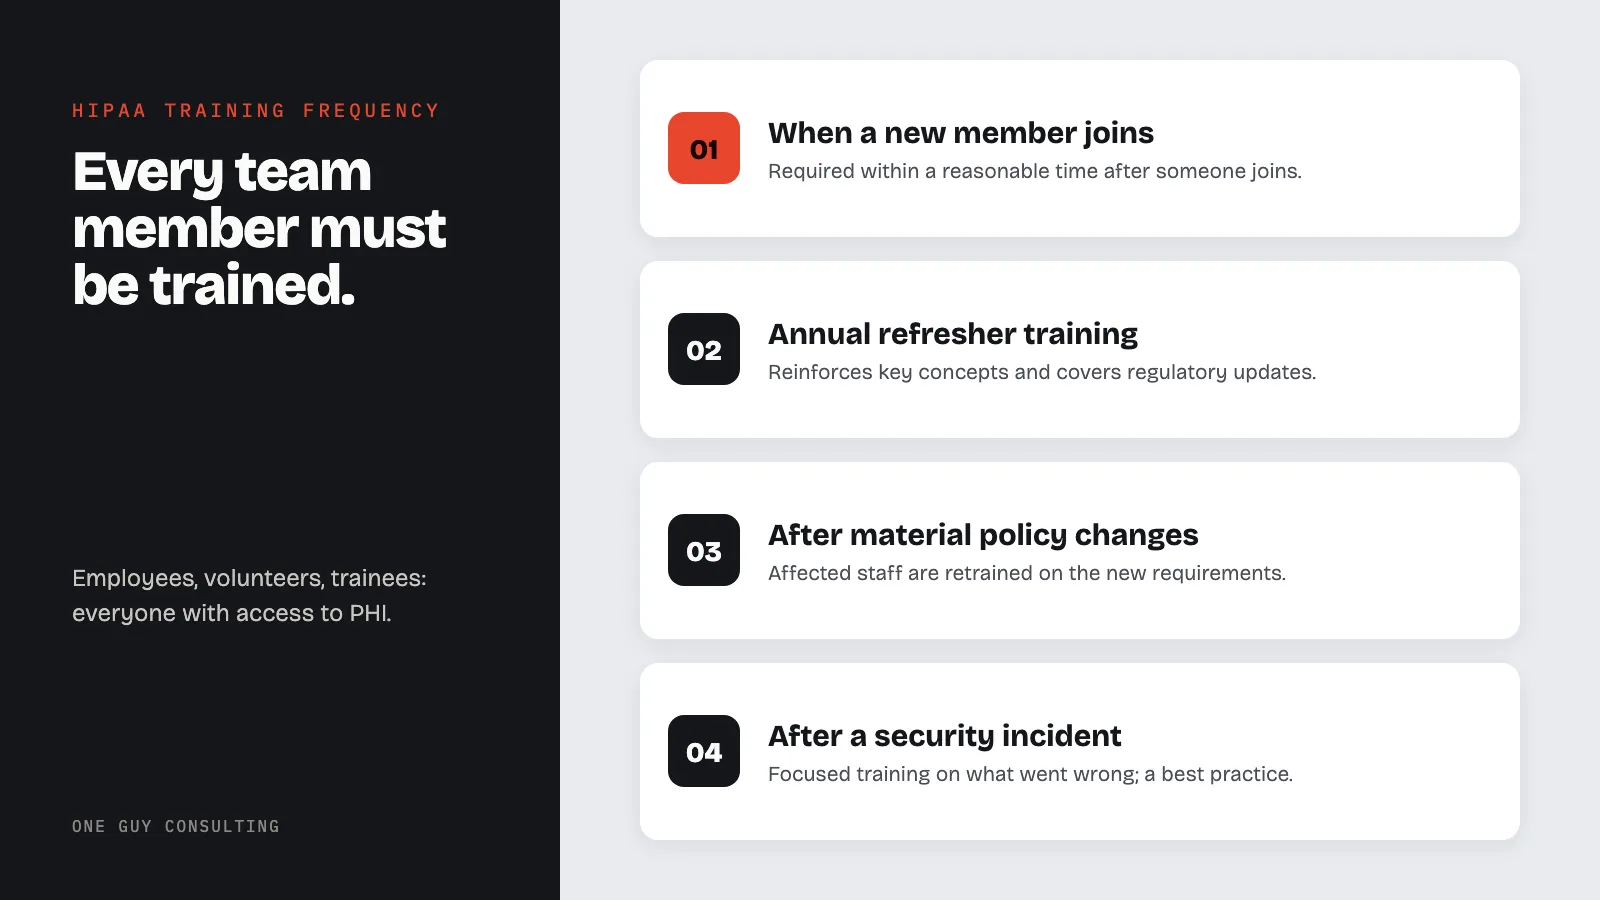
- 01
When a New Member Joins
The Privacy Rule requires training for each new member of the workforce "within a reasonable period of time after the person joins the covered entity's workforce" (45 CFR 164.530(b)(2)(i)(B)). This covers new hires, temps, volunteers, and contractors. Train them during onboarding.
- 02
Annual Refresher Training
HIPAA sets no yearly training interval. The Security Rule's training standard lists "Periodic security updates" as an addressable implementation specification (45 CFR 164.308(a)(5)(ii)(A)) without naming a frequency. An annual refresher is a schedule a practice may choose; it reinforces key concepts, covers regulatory updates, and addresses new threats like phishing and ransomware.
- 03
After Material Policy Changes
When your organization makes material changes to privacy or security policies, affected workforce members must be retrained on the new requirements within a reasonable time frame.
- 04
After a Security Incident
After a breach, near-miss, or security event, run focused training on what went wrong and the related policies. This is a best practice and a key piece of proof for OCR reviews.
Training Modules from One Guy Consulting
Our training is built for small teams. Each annual session uses plain language and comes with tracking and signed attestation records. See the full training module curriculum and completion documentation we deliver.
HIPAA Privacy Rule
What PHI is, the minimum necessary standard, patient rights to access and amend records, and when disclosures are and are not permitted.
HIPAA Security Rule
Password tips, workstation safety, mobile device rules, encryption needs, and access controls.
Breach Notification
How to spot a breach, how to report it inside your practice, what counts as a reportable breach, and the 60-day notice deadline.
Phishing & Social Engineering
How to spot scam emails, phone tricks (vishing), bad links, and how to report them.
Practice-Specific Policies
Your practice's own rules: where PHI is kept, who can access it, how to dispose of it, vendor handling, and contact guidelines.
Role-Based Training
Extra training for specific roles: front desk (check-in, phone calls), billing (claims), and IT (access, backups).
How Training Is Delivered and Documented
Formats to fit your schedule
We offer HIPAA training in several formats to fit your schedule:
- Online self-paced modules: complete anytime, anywhere
- Live virtual sessions: scheduled group training with Q&A
- Recorded sessions: for staff who miss live training
Records that hold up in an audit
Good records are key to audit readiness. Every session produces:
- Completion records: individual attestation for each employee
- Training log: date, topics covered, attendees, trainer name
- Signed acknowledgment: employee signature confirming understanding
- Quiz results: comprehension verification (optional but recommended)
HIPAA does not specify a minimum number of training hours. The requirement is that training be sufficient for the role and cover the policies and procedures relevant to each workforce member's job functions.
Training Questions from Small Practices
How often is HIPAA training required?+
The Privacy Rule requires training for each new workforce member "within a reasonable period of time after the person joins the covered entity's workforce" and for each member whose functions are affected by a material change in the policies or procedures (45 CFR 164.530(b)(2)(i)(B) and (C)). The Security Rule's training standard adds "Periodic security updates" as an addressable implementation specification (45 CFR 164.308(a)(5)(ii)(A)) and sets no interval. Neither section sets a yearly schedule; an annual refresher is a schedule a practice may choose.
Do volunteers and contractors need HIPAA training?+
Yes. HIPAA defines "workforce" broadly. It covers employees, volunteers, trainees, and anyone under your control, paid or not. If they touch PHI, they must be trained.
How long does HIPAA training take?+
HIPAA does not set a length for training. 45 CFR 164.530(b)(1) requires training on the policies and procedures "as necessary and appropriate for the members of the workforce to carry out their functions within the covered entity."
What if an employee refuses to complete training?+
Your Sanctions Policy should cover training refusals. If someone refuses training, do not give them access to PHI. Write down the refusal and what you did about it. This shows you take compliance seriously.
Is online training sufficient, or does it have to be in person?+
HIPAA does not require a specific format. Online, in-person, or a mix all work, as long as the content is thorough, tracked, and understood. Most small practices prefer online self-paced training.
How much does HIPAA training cost?+
HIPAA training is included in both One Guy Consulting plans. The Self-Guided plan ($60/month, $675 per 12 months, or $1,175 per 24 months) includes self-paced training modules on the platform. The Full-Scope plan ($120/month, $1,300 per 12 months, or $2,300 per 24 months) adds 4 hours a month of 1:1 implementation calls with Chuck, a Certified HIPAA Professional, plus incident response guidance and CMS audit response support. There are no per-user fees. See the full pricing breakdown or compare plans.
Ready to Train Your Team?
Book a free 30-minute intro call. We will walk you through how training is assigned and tracked in the platform.