HIPAA FAQ for Small Healthcare Practices
HIPAA Questions Every Small Practice Asks
Whether you are a solo provider, a 5-person medical office, or a growing behavioral health group, these are the HIPAA questions small practices ask most often. Every answer cites the applicable HIPAA regulation.
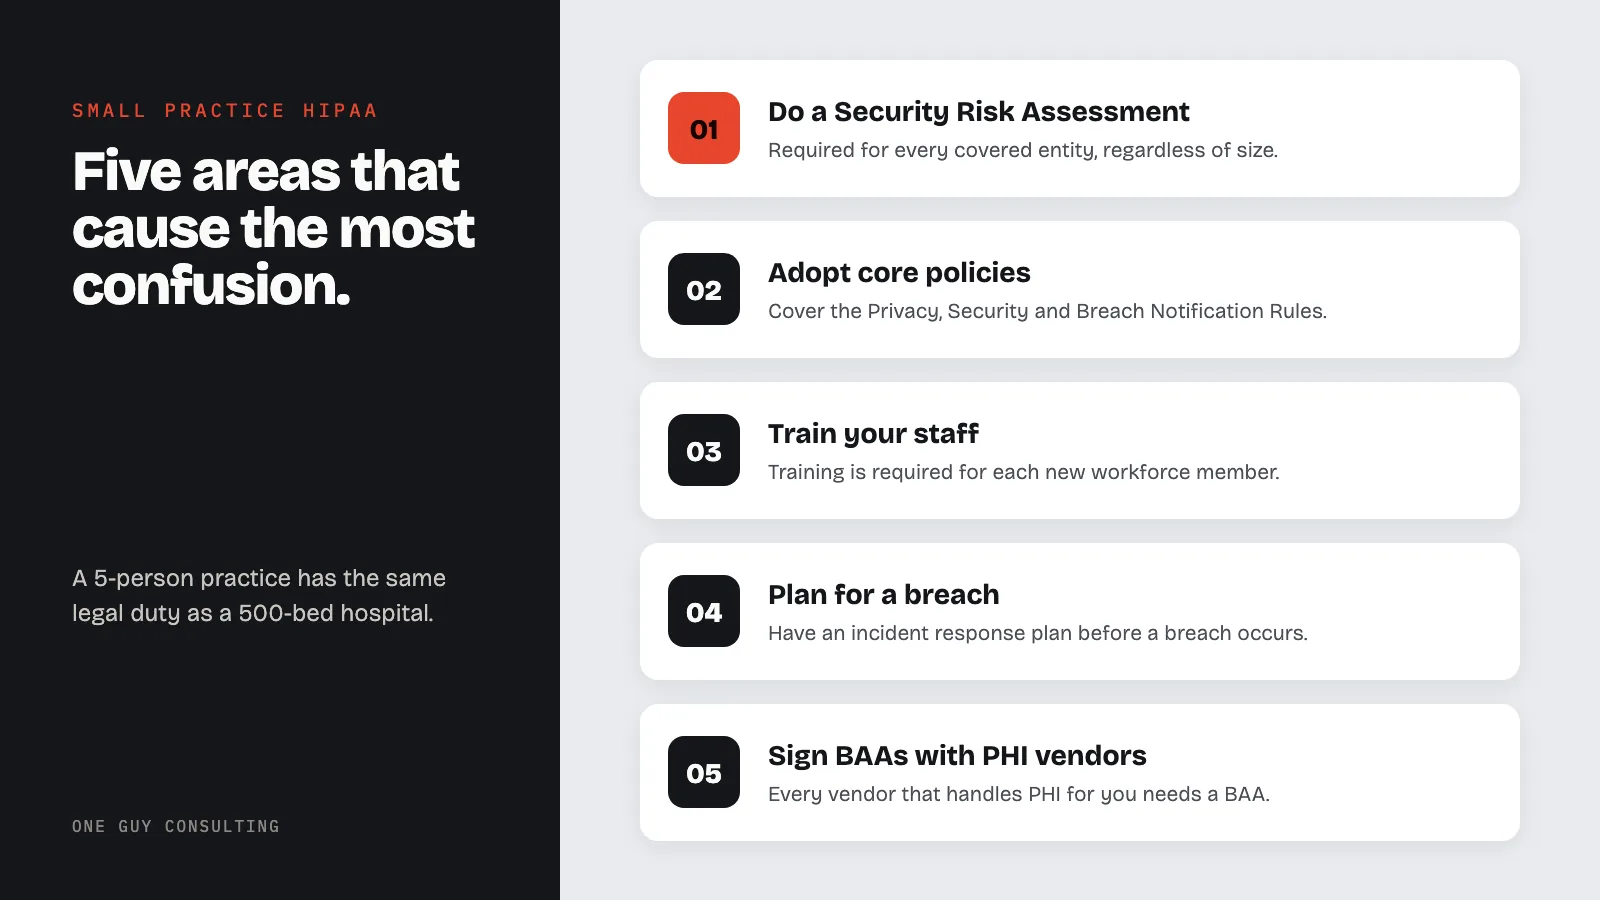
What Small Practices Need to Know
These are the five compliance areas that generate the most confusion for practices with 1 to 20 employees. Each topic links to a detailed answer below.
Security Risk Assessment
Is an SRA required for my practice? What does it involve? How often must it be updated?
Read answers →HIPAA Policies
Which policies are required? Do I need all 100+? What if I already have some?
Read answers →Staff Training
How often is training required? What topics must be covered? What about new hires?
Read answers →Breach Notification
What counts as a breach? Who do I notify? What are the timelines and penalties?
Read answers →BAA & Vendor Management
Which vendors need a BAA? What if a vendor refuses? How do I track them all?
Read answers →Your HIPAA Compliance Questions, Answered
Security Risk Assessment
2 questions01Is a HIPAA Security Risk Assessment required for small practices?+
Yes, with no exceptions. All covered entities and business associates must conduct a Security Risk Assessment regardless of size, as mandated by 45 CFR 164.308(a)(1)(ii)(A). There are no size-based exemptions.
The HHS Office for Civil Rights has stated that failure to perform an SRA is the most common HIPAA violation found during audits and breach investigations. A 5-person medical practice has the same legal obligation as a 500-bed hospital.
The SRA identifies where electronic Protected Health Information (ePHI) is stored, transmitted, and accessed, and documents threats, vulnerabilities, and risk levels for each. Learn about Security Risk Assessment requirements.
02How often does the SRA need to be updated?+
The Security Rule sets no yearly deadline. It requires you to "Review documentation periodically, and update as needed, in response to environmental or operational changes affecting the security of the electronic protected health information" (45 CFR 164.316(b)(2)(iii)), such as a new EHR system, a new office location, or a change in how you store or transmit ePHI.
Each review should reassess threats and vulnerabilities, update the risk register, and document any new mitigation measures. See full pricing details.
HIPAA Policies
2 questions03Which HIPAA policies does a small practice actually need?+
At minimum, small practices need policies covering the HIPAA Privacy Rule, Security Rule, and Breach Notification Rule. The essential policies include:
- Privacy Policy (Notice of Privacy Practices)
- Security Management Process policy
- Access Control and Authorization policy
- Workforce Training policy
- Device and Media Controls policy
- Incident Response and Breach Notification policy
- Business Associate Agreement policy
- Facility Access Controls policy
- Contingency and Disaster Recovery policy
- Sanctions Policy
These ten policies form the minimum foundation. Depending on practice complexity, additional policies may be needed for areas such as audit controls, information system activity review, and transmission security. View the full HIPAA policy template library.
04Do I really need 100+ policies?+
Not necessarily. The number of policies you need depends on the complexity of your practice. A solo provider may need 15 to 20 core policies. A 10-person multi-location practice may need 30 to 40. The key is to adopt policies that match your actual operations and environment rather than using a generic set.
A HIPAA Gap Analysis identifies exactly which policies you are missing so you are not guessing or over-building.
Staff Training
2 questions05How often is HIPAA staff training required?+
The Privacy Rule requires training for each new workforce member "within a reasonable period of time after the person joins the covered entity's workforce" and for each member whose functions are affected by a material change in the policies or procedures (45 CFR 164.530(b)(2)(i)(B) and (C)). The Security Rule's training standard adds "Periodic security updates" as an addressable implementation specification (45 CFR 164.308(a)(5)(ii)(A)) and sets no interval. Neither section sets a yearly schedule; an annual refresher is a schedule a practice may choose.
Training should cover the Privacy Rule, Security Rule, Breach Notification procedures, phishing awareness, and your organization's specific policies.
Training completion should be documented with sign-off attestations proving each employee completed the required material. View HIPAA training requirements.
06What topics must HIPAA training cover?+
Effective HIPAA training covers:
- Privacy Rule basics: what PHI is, minimum necessary standard, patient rights
- Security Rule basics: password policies, workstation security, mobile device handling
- Breach Notification: how to recognize and report a potential breach internally
- Phishing and social engineering: recognizing suspicious emails, phone calls, and links
- Your practice-specific policies: where PHI is stored, who has access, disposal procedures
Training should be documented with sign-off attestations proving each employee completed it.
Breach Notification
2 questions07What happens if my small practice has a data breach?+
A breach is the acquisition, access, use, or disclosure of unsecured PHI in a manner not permitted by the Privacy Rule, as defined in 45 CFR 164.402.
Under the HIPAA Breach Notification Rule, if a breach of unsecured PHI occurs, you must:
- Notify affected individuals within 60 days of discovering a breach, as required by 45 CFR 164.404(b)
- Notify the HHS Secretary via the OCR Breach Portal
- Notify prominent local media if the breach affects 500 or more individuals
For breaches affecting fewer than 500 people, you can submit an annual log to HHS. You must also document your risk assessment of the breach, the individuals affected, what PHI was involved, and your mitigation steps.
Having an incident response plan in place before a breach occurs is essential for meeting these notification deadlines.
08What are the penalties for HIPAA violations?+
HIPAA penalties are tiered based on the level of negligence:
- Tier 1 (Unknowing): $145 to $73,011 per violation
- Tier 2 (Reasonable cause): $1,461 to $73,011 per violation
- Tier 3 (Willful neglect, corrected): $14,602 to $73,011 per violation
- Tier 4 (Willful neglect, not corrected): $73,011 to $2,190,294 per violation
The annual cap per violation category is $2,190,294. Most small practice investigations result from a reported breach or patient complaint. The best defense is a documented compliance program.
BAA & Vendor Management
2 questions09Do I need Business Associate Agreements with all my vendors?+
You need a BAA with every vendor, contractor, or service provider that creates, receives, maintains, or transmits Protected Health Information on your behalf. Common examples include:
- EHR and practice management vendors
- Medical billing companies
- IT support and managed service providers
- Cloud storage services (Google Workspace, Microsoft 365, Dropbox)
- Email providers used for PHI
- Shredding and document destruction companies
- Answering services
- Telehealth platforms
Failure to execute BAAs is one of the most commonly cited HIPAA violations. Practices should maintain a current vendor inventory that identifies which vendors have access to PHI and tracks BAA execution status. Learn more about BAA management.
10What if a vendor refuses to sign a BAA?+
If a vendor handles PHI and refuses to sign a BAA, you cannot use that vendor for PHI-related services. HIPAA is clear: no BAA means no PHI access. You have three options:
- Escalate the request: sometimes the initial contact does not know the company offers BAAs. Ask for their compliance or legal team.
- Find an alternative vendor: many competitors in every category offer BAAs as standard.
- Restructure the workflow: if the vendor does not need to touch PHI, remove PHI from the data they handle.
Evaluating vendor BAA readiness before signing a contract prevents compliance gaps later. Learn about vendor management.
Cost & Getting Started
4 questions11How much does HIPAA compliance cost for a small practice?+
One Guy Consulting offers flat-rate pricing for small practices: two plans, each with three ways to pay.
- Self-Guided Plan: $60 per month, $675 per 12 months, or $1,175 per 24 months. Platform only, no consulting time: compliance toolkit, policy templates, training modules, risk assessment tools, and vendor management features.
- Full-Scope Plan: $120 per month, $1,300 per 12 months, or $2,300 per 24 months. Everything in Self-Guided plus 4 hours per month of 1:1 implementation calls with Chuck Weiselberg, a Certified HIPAA Professional, including a guided SRA, gap analysis, staff training facilitation, incident response guidance, and CMS audit response support.
There are no per-user fees, no setup fees, and no hidden charges. Pricing is based on practice scope, not headcount. See the full pricing breakdown.
12Can a small practice handle HIPAA compliance without a consultant?+
Yes, but it requires significant time and expertise. HIPAA compliance involves understanding the Privacy Rule, Security Rule, and Breach Notification Rule, then applying them to your specific environment. You need to complete a Security Risk Assessment, write or adopt policies, train your staff, execute Business Associate Agreements, and maintain documentation for at least six years.
Many small practices lack the bandwidth to manage this alongside patient care. Whether handled internally or with outside help, the key is a systematic, documented approach. Compare compliance plan options.
13How long does it take a small practice to become HIPAA compliant?+
For small practices with 1 to 20 employees, reaching a compliant baseline typically takes weeks, not months with dedicated effort. This includes completing the Security Risk Assessment, gap analysis, policy adoption, initial staff training, and vendor BAA review.
Self-directed implementations typically take 3 to 6 months depending on how much time the team dedicates each week. A compliance tracker helps ensure no required steps are missed.
14What happens if my practice fails an OCR audit?+
If the HHS Office for Civil Rights (OCR) investigates your practice and finds HIPAA violations, penalties range from $145 per violation up to $2,190,294 per violation category per year for willful neglect.
The best defense is a documented compliance program showing your Security Risk Assessment, policies, training records, and BAA inventory. Organizations that can demonstrate ongoing good-faith compliance efforts are treated more favorably during investigations.
No questions match that search. Try a shorter word, check the glossary, or ask Chuck directly.
Still Have Questions About HIPAA Compliance?
Book a free 30-minute intro call. We will review your practice, answer your specific HIPAA questions, and explain exactly what compliance looks like for your situation.