Three HIPAA Training Modules for Your Team
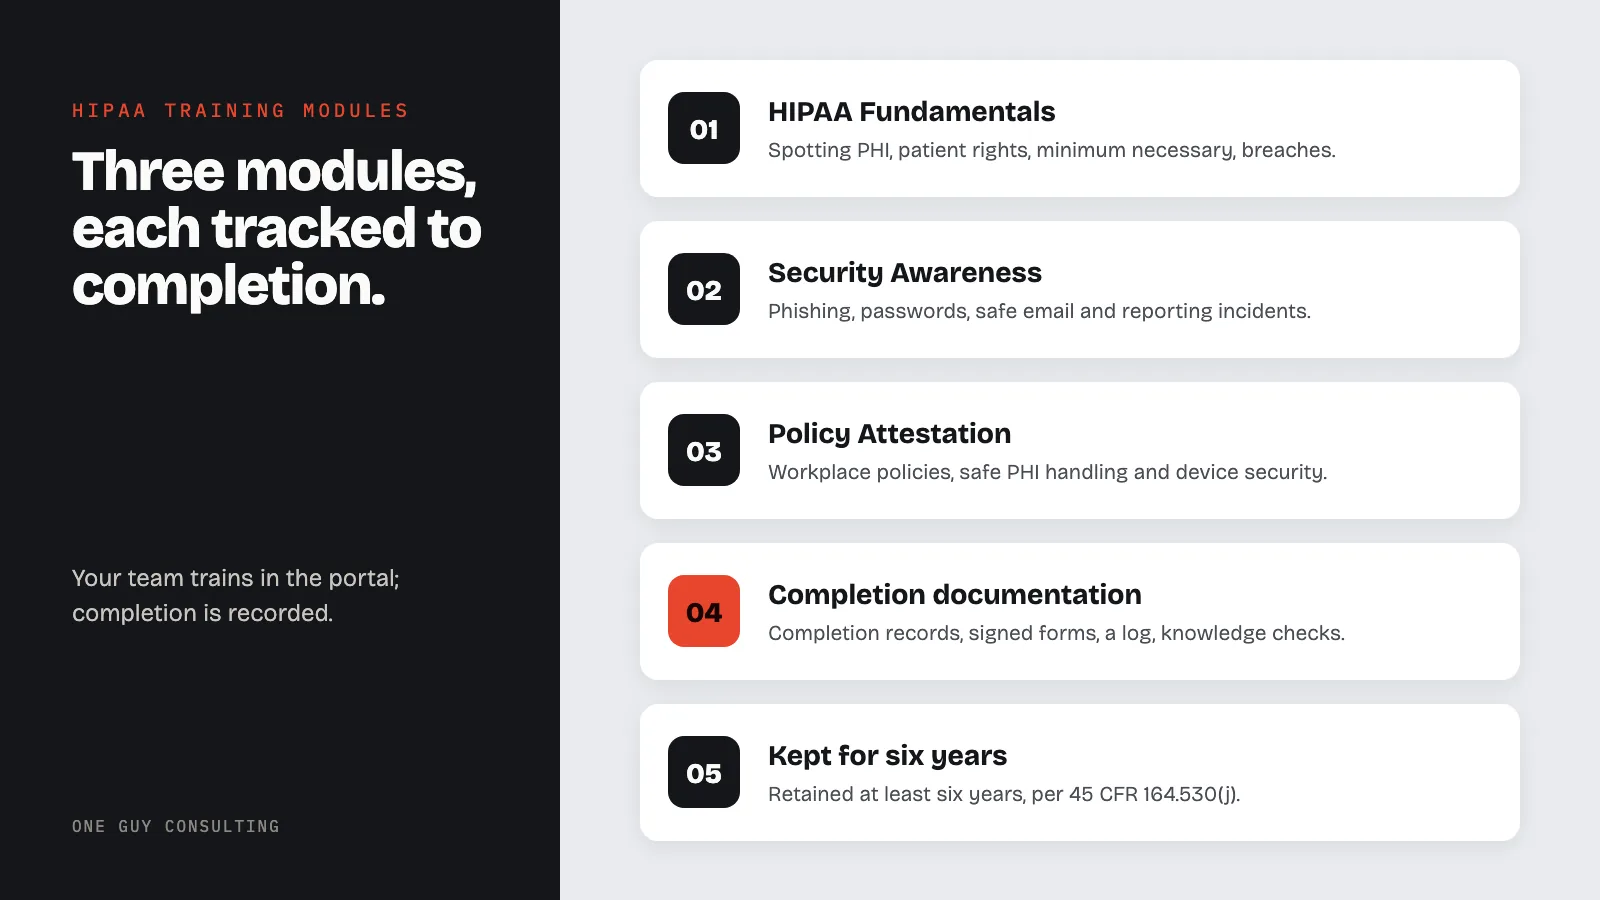
Three focused training modules built for small healthcare teams. Each covers one clear compliance area your team needs to know, with knowledge checks and completion tracking.
HIPAA 101 Training
HIPAA Fundamentals
Core HIPAA privacy and security concepts every team member needs to know. Covers how to spot PHI, patient rights, the minimum necessary standard, and breach notification requirements.
Learn More About HIPAA FundamentalsCyber Security
Security Awareness
Spot phishing, social engineering, and common cyber threats aimed at healthcare teams. Learn password best practices, safe email habits, and how to report incidents.
Learn More About Security AwarenessStaff Training
Policy Attestation
Covers workplace policies, safe PHI handling, device security, and the compliance duties specific to your practice.
Learn More About Policy AttestationWhat Your Team Will See
Your team completes training through our portal. Each module tracks progress, includes knowledge checks, and records completion for you.
Training Portal Landing
Staff see their assigned courses and status at a glance.
HIPAA 101 Module
Structured sections with clear progress indicators.
Cybersecurity Awareness
Covers phishing, social engineering, and ransomware.
HIPAA 101 Training
Introduction to HIPAA
What HIPAA is, who it applies to, and why it matters for every role on your team.
- Covered entities and business associates
- Privacy Rule overview
- Security Rule overview
Protected Health Information
How to identify, handle, and safeguard PHI in daily workflows.
- 18 PHI identifiers
- Minimum necessary standard
- Permitted uses and disclosures
Breach Notification
What constitutes a breach and the reporting obligations under federal law.
- Breach identification
- Notification timelines
- Documentation requirements
Cybersecurity Awareness
Common Threats
The attacks that most often hit healthcare teams.
- Phishing and spear phishing
- Ransomware
- Social engineering
Password and Access Security
Simple habits that block unauthorized access to systems and data.
- Strong password practices
- Multi-factor authentication
- Screen lock and session management
Incident Response
What to do when something looks wrong and how to report it.
- Recognizing suspicious activity
- Internal reporting procedures
- Containment basics
Policy Attestation
Policy Review
Walk through your own HIPAA policies and procedures.
- Privacy policies
- Security policies
- Acceptable use policies
PHI Handling Procedures
Role-based guidance on how to handle, store, and send PHI.
- Physical safeguards
- Electronic safeguards
- Disposal procedures
Acknowledgement and Sign-Off
Record that each team member has read and understood their duties.
- Digital attestation
- Completion tracking
- Audit-ready records
Training Completion Documentation
Every training session creates audit-ready records. OCR asks for these records during compliance reviews and breach investigations.
- Individual Completion Records: Employee name, training date, module completed, and facilitator name. One record per person, per session.
- Signed Acknowledgment Forms: Each employee signs a form to confirm they got the training and understand their duties.
- Training Log: Master log with training dates, topics, attendee names, and trainer for each session. Kept as a running record.
- Knowledge Check Results: Quiz scores that show each person understood the material. Proof that training went beyond showing up.
- Attestation Statements: Ties each completed training to the exact policy versions in effect at the time.
When Training Must Be Delivered
- 01
Before First PHI Access
New hires must complete HIPAA training before they access any protected health information. This is required under 45 CFR 164.530(b)(1), not a best practice suggestion.
- 02
Annual Refresher
At least once per year, based on HHS's interpretation of "periodic" training. Annual refreshers keep skills sharp and lock in key concepts that drift over time.
- 03
After Material Policy Changes
When policies change in ways that affect how staff handle PHI, those staff members must be retrained on the changes. Waiting for the next annual cycle is not enough.
- 04
After a Security Incident
When an incident reveals a training gap, focused retraining on that issue should follow. This closes the gap and shows a corrective response if OCR reviews the incident.
For a detailed breakdown of training frequency requirements, see our training frequency guide for small practices.
What the Regulation Requires for HIPAA Training
- Privacy Rule training standard (45 CFR 164.530(b)(1))
- A covered entity must train all members of its workforce on its policies and procedures for protected health information, as necessary and appropriate for each person to carry out their job functions.
- Timing (45 CFR 164.530(b)(2)(i))
- Each new workforce member must be trained within a reasonable period of time after joining, and any workforce member whose functions are affected by a material change in policies or procedures must be retrained within a reasonable period after the change takes effect.
- Security awareness and training standard (45 CFR 164.308(a)(5)(i))
- Implement a security awareness and training program for all members of the workforce, including management. Its four addressable implementation specifications are security reminders, protection from malicious software, log-in monitoring, and password management (164.308(a)(5)(ii)(A) through (D)).
- Documentation (45 CFR 164.530(b)(2)(ii) and 164.530(j))
- The covered entity must document that the training was provided and retain that documentation for six years from the date it was created or last in effect, whichever is later. Security Rule documentation carries the same six-year retention requirement under 45 CFR 164.316(b)(2)(i).
- Business associates
- The Security Rule, including its training standard, applies to business associates as well as covered entities (45 CFR 164.302). Read the regulation text at eCFR 164.530 and eCFR 164.308.
Training Documentation FAQ
What documentation proves my staff received HIPAA training?+
Audit-ready proof includes completion records, signed acknowledgment forms, a master training log, and knowledge check results. Together these records show that training was delivered, received, and understood. Under 45 CFR 164.530(j), covered entities must retain this documentation for at least six years.
How long must training records be retained?+
Six years minimum. Under 45 CFR 164.530(j), covered entities must retain training documentation for six years from the date of creation or the date it was last in effect, whichever is later. Many keep records longer as a practical safeguard against delayed investigations.
What happens if an employee refuses to complete training?+
HIPAA requires that all workforce members receive training. If an employee refuses, the practice must apply its sanction policy under 45 CFR 164.308(a)(1)(ii)(C). Document the refusal, the steps taken to address it, and any sanctions applied. An untrained workforce member with access to PHI represents a compliance gap.
Do new hires need training before their first day?+
Training must be completed before the new hire accesses PHI, though not always before their first day. If their first day includes PHI access, then yes, training must come first. Many practices schedule training as part of orientation before granting system access.
Does HIPAA require a specific number of training hours?+
No. HIPAA does not set a minimum number of training hours. The standard requires training that is "necessary and appropriate" for each workforce member's job functions. Content depth and relevance matter more than seat time. Our modules are built to be thorough without running long.
Can online training satisfy the HIPAA requirement?+
Yes. HIPAA does not require one delivery format. Online, in-person, or hybrid training all satisfy the rule as long as the content fits each role, completion is tracked, and records are kept. The key is proving that each person completed the training and understood the material.
Ready to Train Your Team?
Book a short intro and we will match the right training modules to your team size and compliance needs.