FAQ

HIPAA Compliance FAQ for Covered Entities and Business Associates

Plain answers to the HIPAA questions we hear most: risk assessments, BAAs, written policies, staff training, and how to report an incident. For covered entities and business associates alike.
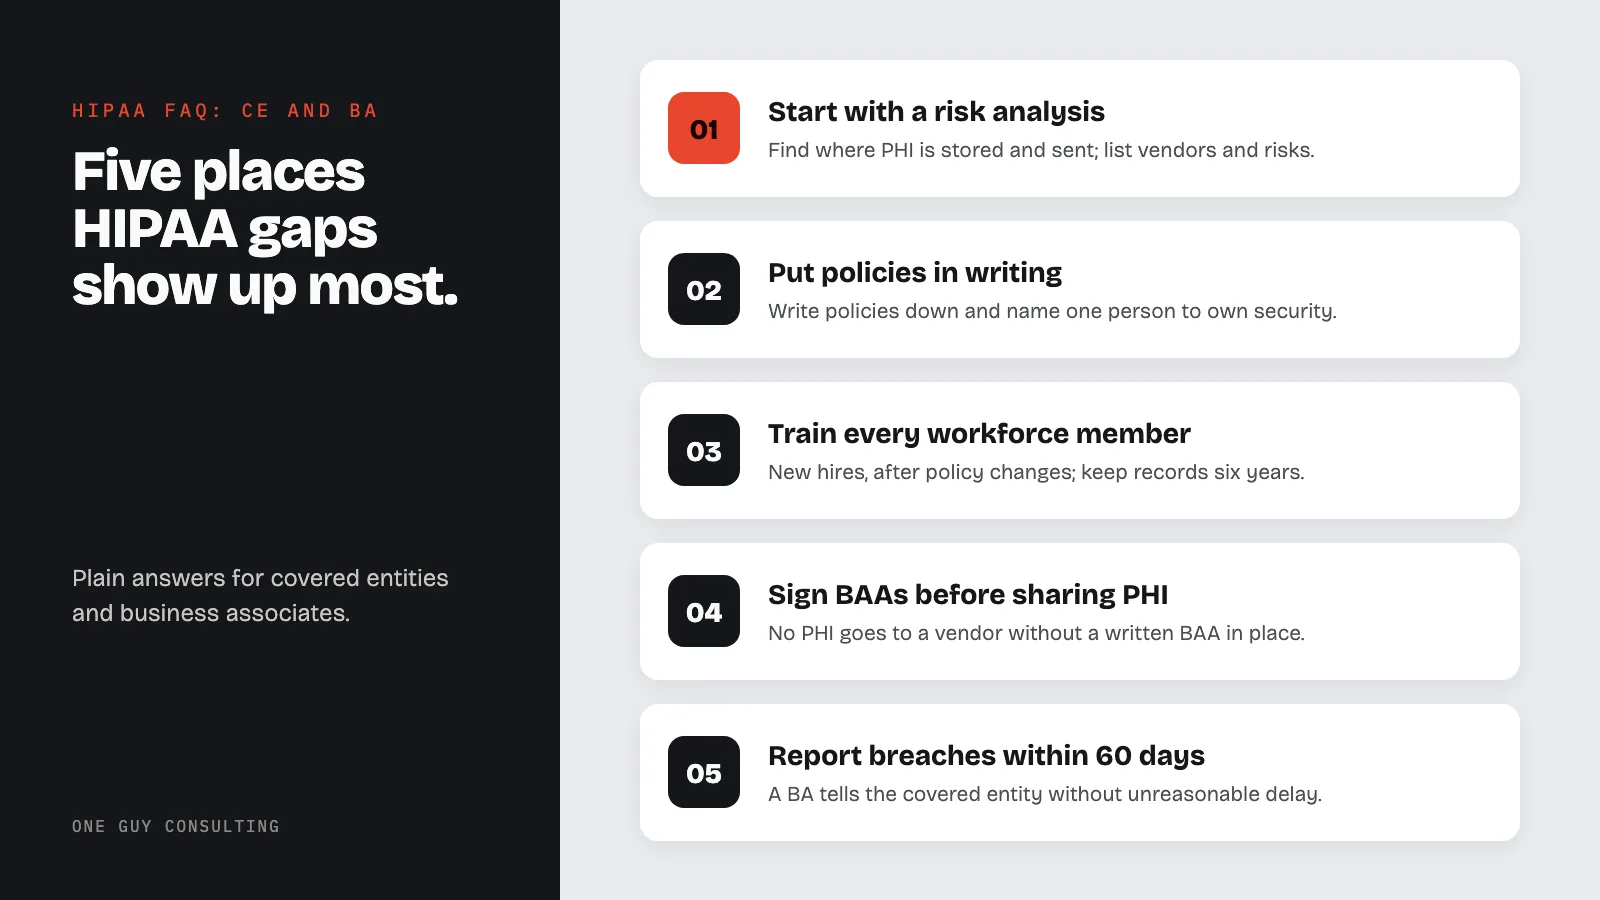
Diagram: the five places HIPAA gaps show up most for covered entities and business associates: start with a risk analysis, put policies in writing, train every workforce member, sign BAAs before sharing PHI, report breaches within 60 days.
Overview

Common HIPAA Questions from Healthcare Practices and Their Vendors

Run a small clinic? A dental office? A behavioral health practice? Or a firm that handles protected health information for a provider? The same HIPAA rules reach all of you. The questions below cover the spots where gaps show up most: Security Risk Assessments, written policies and procedures, workforce training, Business Associate Agreements, and incident reporting.

Who is this page for? A covered entity is a health care provider, a health plan, or a health care clearinghouse. A business associate is a firm or a person that creates, receives, maintains, or transmits protected health information (PHI) for a covered entity. Think IT vendors, billing services, cloud storage firms, and shredding companies.

FAQ

HIPAA Compliance Questions and Answers

01 / 02

For Covered Entities

5 questions
01What HIPAA compliance help does One Guy Consulting offer for small healthcare practices?+
One Guy Consulting covers the whole job for small practices and business associates: a Security Risk Assessment, gap analysis and remediation plans, custom policies and procedures, staff training with tracking, site and IT audits, vendor and BAA management, incident handling, and help getting ready for an audit. It is all in one flat yearly rate. No per-user fees.
02What do I do if my clinic has no HIPAA risk assessment or written policies?+
No risk assessment and no written policies yet? Start with a Security Risk Analysis. Find where PHI is stored and sent. List your vendors and devices. Write down the main risks. Then put the policies and procedures in writing, and name one person to own security. The Security Risk Analysis is called for under 45 CFR 164.308(a)(1)(ii)(A), and written policies under §164.316(a). Those two steps hold up everything else.
03What is a Security Risk Assessment and is it required?+
A Security Risk Assessment (SRA) is a written review of what could go wrong with the confidentiality, integrity, and availability of the electronic protected health information (ePHI) you hold. It is called for under 45 CFR 164.308(a)(1)(ii)(A) for every covered entity and business associate. It has to find where ePHI is created, received, maintained, or transmitted, weigh what you have in place now, judge how likely each threat is and how much it would hurt, and give every weak spot a risk level. It is not a one-and-done job: review it on a cycle, and again any time your setup shifts.
04Does HIPAA require staff training?+
Yes. The HIPAA Security Rule at 45 CFR 164.308(a)(5)(i) says a covered entity and a business associate both have to run a security awareness and training program for every workforce member, managers included. The Privacy Rule at §164.530(b) adds training on your own privacy policies and procedures. Train each new hire within a reasonable time, and again any time a policy changes in a way that touches their job. Write down every session, and keep the records at least six years per §164.530(j).
05What happens if we don't have BAAs with our vendors?+
Under 45 CFR 164.502(e), a covered entity cannot hand protected health information to a business associate, or let one create, receive, maintain, or transmit PHI for it, without a written Business Associate Agreement (BAA) in place. Running without BAAs for vendors that touch PHI is a gap OCR has cited in enforcement actions. And if a breach comes through a vendor you never signed, expect a harder look for the missing agreement. The BAA has to say how PHI may be used and disclosed, call for safeguards, and set out breach notice.
02 / 02

For Business Associates

3 questions
06What HIPAA requirements apply to business associates?+
Since the HITECH Act and the 2013 Omnibus Rule, a business associate answers directly for much of the HIPAA Security Rule and for parts of the Privacy Rule. Under 45 CFR 164.502(e) and 164.308(b), a business associate has to put administrative, physical, and technical safeguards in place, run its own Security Risk Assessment under §164.308(a)(1)(ii)(A), write and keep policies and procedures per §164.316(a), train their workforce per §164.308(a)(5)(i), report incidents and breaches to the covered entity per §164.314(a)(2)(i)(C), and sign BAAs with any subcontractor that reaches PHI. The civil and criminal penalties are the same ones a covered entity faces.
07Does a business associate need its own Security Risk Assessment?+
Yes. Under 45 CFR 164.308(a)(1), every business associate has to run its own careful, thorough review of what could go wrong with the confidentiality, integrity, and availability of the ePHI it holds. It is the same duty a covered entity carries. You cannot lean on the covered entity's risk assessment; yours has to look at your own systems, your workflows, your workforce, and your building. Review it again when your work, your tech, or the threats around you change.
08What should a business associate do about incident reporting?+
Under 45 CFR 164.410, a business associate that finds a breach of unsecured PHI tells the covered entity without unreasonable delay, and no later than 60 days after it finds out. The notice has to name who was affected, if you know, say what kinds of data were involved, describe what happened and what you are doing about it, and say what those people should do to protect themselves. The covered entity then tells the people affected, under §164.404. Keep a written incident response plan, train your workforce to spot and report a possible breach, and log every security incident, whether or not it rises to a reportable breach.

No questions match that search. Try a shorter word, check the glossary, or ask Chuck directly.

Have a HIPAA Question We Did Not Cover?

Book a free 30-minute call. We will look at where you are and tell you what to do next, whether you are a covered entity or a business associate.

OGC-BotHi! What can I help you with?