HIPAA Audit Readiness for Small Practices
What OCR Auditors Look For and How to Prepare Without Overbuilding
Most small practice investigations are triggered by a breach report or patient complaint. Here is how the audit process works, what documents you need, and how to stay ready without building a compliance program you cannot maintain.
How OCR HIPAA Audits Work for Small Practices
Small healthcare practices are subject to the same HIPAA audit standards as large hospital systems. OCR does not exempt organizations based on size. Audits can be triggered by breach reports, patient complaints, or random selection.
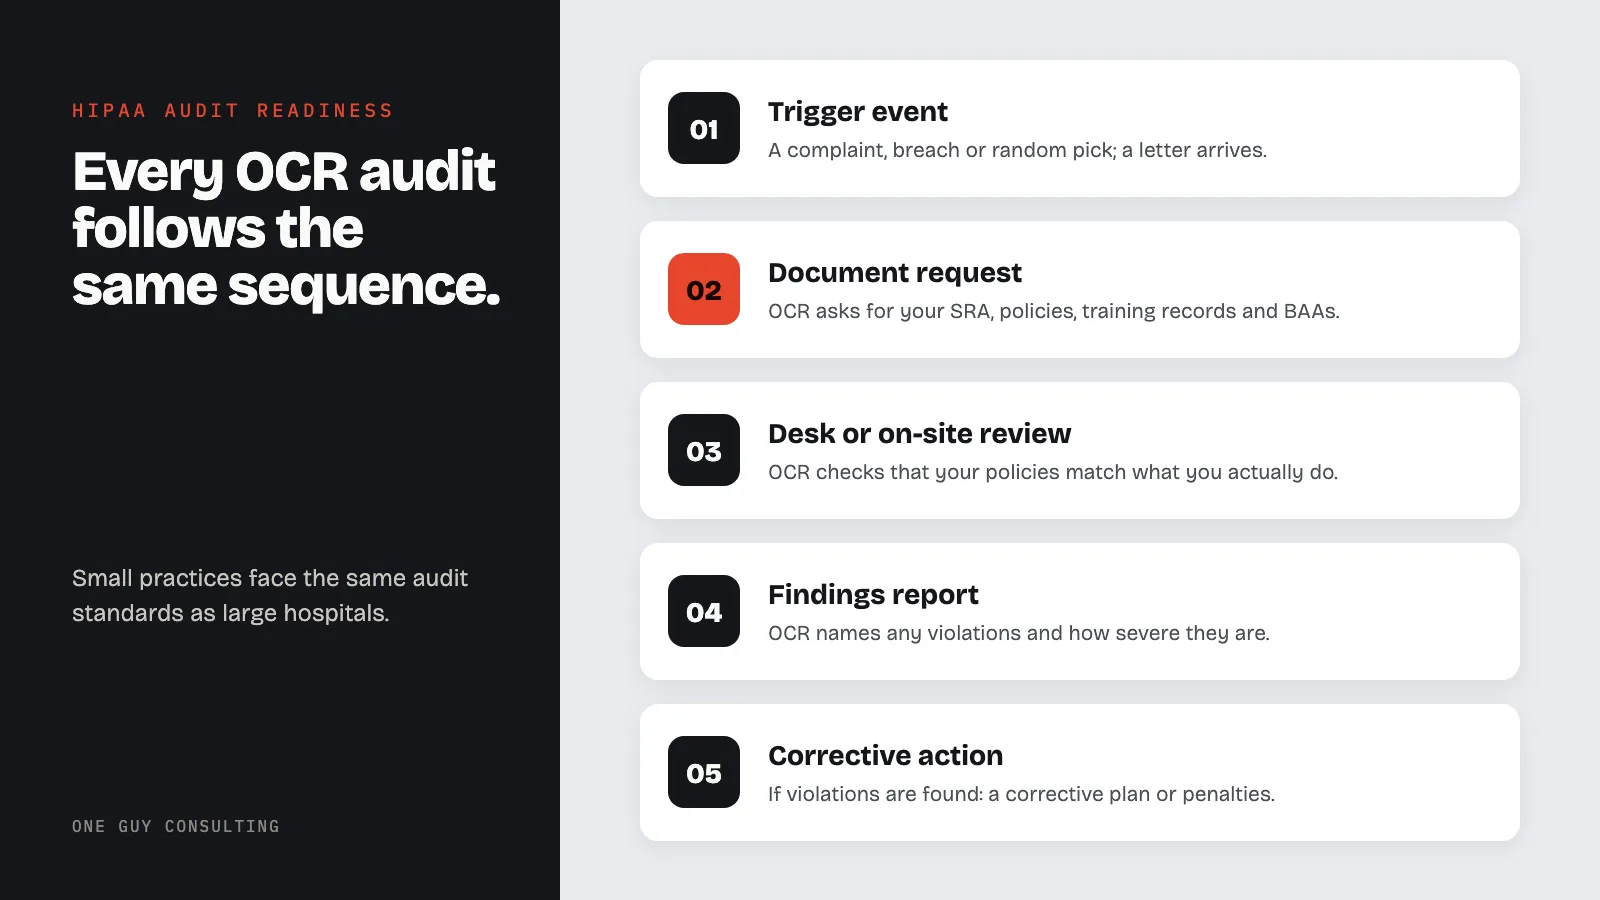
The HHS Office for Civil Rights (OCR) enforces HIPAA through complaint investigations, breach reviews, and compliance audits. The audit process follows a consistent sequence regardless of organization size.
Trigger Event
A patient complaint, reported breach, or random audit selection initiates the OCR investigation. You receive a formal notification letter.
Document Request
OCR sends a detailed list of documents to produce: SRA, policies, training records, BAA inventory, breach logs, and incident documentation.
Desk or On-Site Review
OCR reviews your documentation (desk audit) or visits your location (on-site audit) to verify that your policies match your actual practices.
Findings Report
OCR issues findings identifying any violations, their severity, and whether they constitute willful neglect, reasonable cause, or unknowing violations.
Corrective Action
If violations are found, OCR may require a Corrective Action Plan (CAP), impose civil monetary penalties, or negotiate a resolution agreement.
Monitoring Period
After resolution, OCR may monitor your compliance for 1 to 3 years to verify that corrective actions are implemented and sustained.
Documents OCR Auditors Request from Small Practices
If you can produce every item on this list within 48 hours of an OCR request, your practice is audit-ready. These are the documents OCR auditors routinely request during investigations and compliance reviews. For a version you can work through item by item, use the HIPAA audit readiness checklist.
The documents OCR asks for
NoteTick items as you go. Your progress stays in this browser only.
Where Small Practices Most Often Fall Short
No Security Risk Assessment
The single most common HIPAA violation. Many small practices have never completed an SRA or have not updated it in years. This is the first document OCR requests.
Policies Downloaded but Not Adopted
Having generic policy templates in a folder is not compliance. Policies must be implemented and "reasonably designed, taking into account the size and the type of activities that relate to protected health information undertaken by a covered entity" (45 CFR 164.530(i)(1)). Security Rule policies must be kept "in written (which may be electronic) form" and made "available to those persons responsible for implementing the procedures to which the documentation pertains" (45 CFR 164.316(b)(1)(i) and (b)(2)(ii)).
No Training Documentation
Saying "we train our staff" without attestation records means you cannot prove it. OCR requires signed acknowledgments and training logs.
Missing or Incomplete BAAs
Many practices have BAAs with their EHR vendor but miss billing services, cloud storage, IT support, and email providers that also handle PHI.
HIPAA Penalty Tiers for Audit Violations
OCR imposes civil monetary penalties based on the level of culpability. Penalty amounts are adjusted annually for inflation. The four tiers defined under 45 CFR 160.404 are:
| Tier | What it means | Penalty |
|---|---|---|
| Tier 1: Lack of Knowledge | The covered entity did not know and, by exercising reasonable diligence, would not have known of the violation. | $145 to $73,011 per violation |
| Tier 2: Reasonable Cause | The violation was due to reasonable cause and not willful neglect. | $1,461 to $73,011 per violation |
| Tier 3: Willful Neglect, Corrected | The violation was due to willful neglect but was corrected within 30 days of discovery. | $14,602 to $73,011 per violation |
| Tier 4: Willful Neglect, Not Corrected | The violation was due to willful neglect and was not corrected within 30 days. Annual caps apply per violation category. | $73,011 per violation |
Key HIPAA Audit Terms Defined
- Office for Civil Rights (OCR)
- The office within the U.S. Department of Health and Human Services that enforces the HIPAA Privacy, Security, and Breach Notification Rules (45 CFR Parts 160 and 164).
- Complaint investigation
- Any person who believes a covered entity or business associate is not complying with HIPAA may file a written complaint with HHS, which may then investigate (45 CFR 160.306). Most small-practice enforcement begins with a complaint or a breach report.
- Compliance review
- An HHS review of whether a covered entity or business associate is complying with HIPAA. HHS will conduct one when a preliminary review of the facts indicates a possible violation due to willful neglect, and may conduct one in any other circumstance (45 CFR 160.308).
- Corrective action plan (CAP)
- When an investigation or compliance review indicates noncompliance, HHS may resolve the matter by informal means, including a completed corrective action plan or other agreement (45 CFR 160.312(a)(1)). A resolution agreement is the settlement document that typically carries the CAP and any payment.
- Civil money penalty (CMP)
- The fine HHS may impose when a matter is not resolved informally, in tiered amounts based on the level of culpability (45 CFR 160.404). The current tiers are listed in the penalty section above.
- Documentation retention
- Privacy Rule documentation must be kept for six years from its creation or the date it was last in effect, whichever is later (45 CFR 164.530(j)(2)). Security Rule documentation has the same six-year rule (45 CFR 164.316(b)(2)(i)). Read the enforcement rules at eCFR Part 160, Subpart C.
Audit Readiness Questions
How do OCR HIPAA audits work for small practices?+
Audits are typically triggered by breach reports, patient complaints, or random selection. OCR sends a notification letter, requests documentation, conducts a desk or on-site review, issues findings, and may require corrective action. Small practices receive the same scrutiny as large organizations.
How long does a HIPAA audit take?+
A desk audit typically takes 30 to 60 days from notification to findings. On-site audits may take 1 to 3 days on location. The full process from notification to resolution can span 3 to 12 months depending on findings and corrective actions required.
Can a small practice prepare for an audit without a consultant?+
Yes, but it requires significant time and HIPAA knowledge. The key is having complete, current documentation. One Guy Consulting's Self-Guided plan ($60/month, $675 per 12 months, or $1,175 per 24 months) provides the platform, tools, and structure, with no consulting time. The Full-Scope plan ($120/month, $1,300 per 12 months, or $2,300 per 24 months) adds 4 hours a month of 1:1 implementation calls with Chuck, incident response guidance, and CMS audit response support. See the full pricing breakdown or compare plans.
What are the penalties if my practice fails an OCR audit?+
HIPAA penalties follow four tiers based on culpability: Tier 1 (lack of knowledge) ranges from $145 to $73,011 per violation; Tier 2 (reasonable cause) from $1,461 to $73,011; Tier 3 (willful neglect, corrected) from $14,602 to $73,011; and Tier 4 (willful neglect, not corrected) is $73,011 per violation with annual caps per category. Most small practice cases result in corrective action plans rather than maximum fines, especially when the practice demonstrates good-faith compliance efforts.
Get Audit-Ready With Confidence
Book a free 30-minute intro call. We will assess your current compliance state and show you exactly what documentation you need to be audit-ready.