The Complete HIPAA Compliance Process
Eight steps from discovery through annual sustainment, with CFR citations and realistic timelines for small healthcare practices. This is the systematic approach OCR expects to see.
Why a Defined Compliance Process Matters
OCR does not just check whether you have individual safeguards in place. They evaluate whether your organization follows a systematic, documented approach to protecting patient information. The Security Rule under 45 CFR 164.306(a) requires covered entities and business associates to ensure the confidentiality, integrity, and availability of all ePHI they create, receive, maintain, or transmit.
A defined process turns compliance from a guessing game into an operational system.
Each step builds on the previous one. Skipping steps or addressing them out of order creates gaps that OCR specifically looks for during investigations.
If you are starting from scratch or unsure where your practice stands, our HIPAA starting point guide covers the first priorities. For a phased checklist approach, see the HIPAA starter checklist.
Eight Steps to HIPAA Compliance
- 01
Discovery & Scope Assessment
Identify the boundaries of your compliance program: which locations, systems, and workforce members handle PHI. Document your current state against the requirements of 45 CFR 164.306(a). This determines what the remaining seven steps need to cover.
HIPAA gap analysis servicesKey deliverablesPHI inventory, system inventory, workforce roster, scope document. - 02
Security Risk Assessment
Conduct a thorough SRA as required by 45 CFR 164.308(a)(1)(ii)(A). Identify every system, device, and workflow that stores, transmits, or accesses ePHI. Document threats and vulnerabilities, rate risk levels, and create a prioritized remediation plan. This is the most commonly cited deficiency in OCR enforcement actions. See how the gap analysis and remediation plan are built from the SRA.
Security Risk Assessment requirements and processKey deliverablesCompleted SRA report, risk register, remediation plan with timelines. - 03
Policy & Procedure Development
Develop written policies and procedures that comply with the Security Rule as required by 45 CFR 164.316(a). Policies must reflect how your practice actually operates, not how a generic template assumes you operate. At minimum, cover privacy, security management, access control, training, device controls, incident response, BAA management, facility access, contingency planning, and sanctions.
HIPAA policy templates for small practicesKey deliverablesCustomized policy manual, procedure documents, adoption records. - 04
Workforce Training
Train every workforce member who handles PHI before they access patient information, as required by 45 CFR 164.308(a)(5)(i). Training must cover the Privacy Rule, Security Rule, breach reporting, phishing awareness, and your practice-specific policies. Document completion with signed attestations and schedule annual refresher training.
HIPAA training requirements and program detailsKey deliverablesTraining curriculum, completion records, signed attestations, refresher schedule. - 05
BAA Management
Identify every vendor and subcontractor that creates, receives, maintains, or transmits PHI on your behalf. Execute Business Associate Agreements as required by 45 CFR 164.502(e) and 164.308(b)(1). Maintain a current BAA inventory and review vendor compliance annually.
BAA management and vendor complianceKey deliverablesVendor inventory, executed BAAs, annual review schedule. - 06
Incident Response & Breach Preparedness
Establish an incident response plan covering breach identification, containment, risk assessment, notification timelines, and documentation. Meet the notification requirements of 45 CFR 164.404(b), 164.406, and 164.408. Conduct tabletop exercises so your team knows what to do before a breach occurs.
Incident response and breach managementKey deliverablesIncident response plan, notification procedures, tabletop exercise records. - 07
Evidence Packaging & Documentation
Organize and retain all compliance documentation for at least six years as required by 45 CFR 164.530(j). This includes your completed SRA, written policies, training records, BAA inventory, incident reports, and remediation evidence. If OCR investigates, this documentation is your evidence of a systematic compliance effort.
Documentation requirements and starting pointKey deliverablesOrganized compliance binder, document retention schedule, evidence index. - 08
Annual Review & Sustainment
Review and update your entire compliance program at least annually, as required by 45 CFR 164.530(a)(1) and 164.308(a)(2). Reassess risks when systems or workflows change, update policies accordingly, retrain staff, verify BAA currency, and test your incident response plan. Compliance is not a one-time project.
Vendor management and annual review servicesKey deliverablesAnnual review report, updated SRA, policy revision log, training refresher records.
How Long Does This Take?
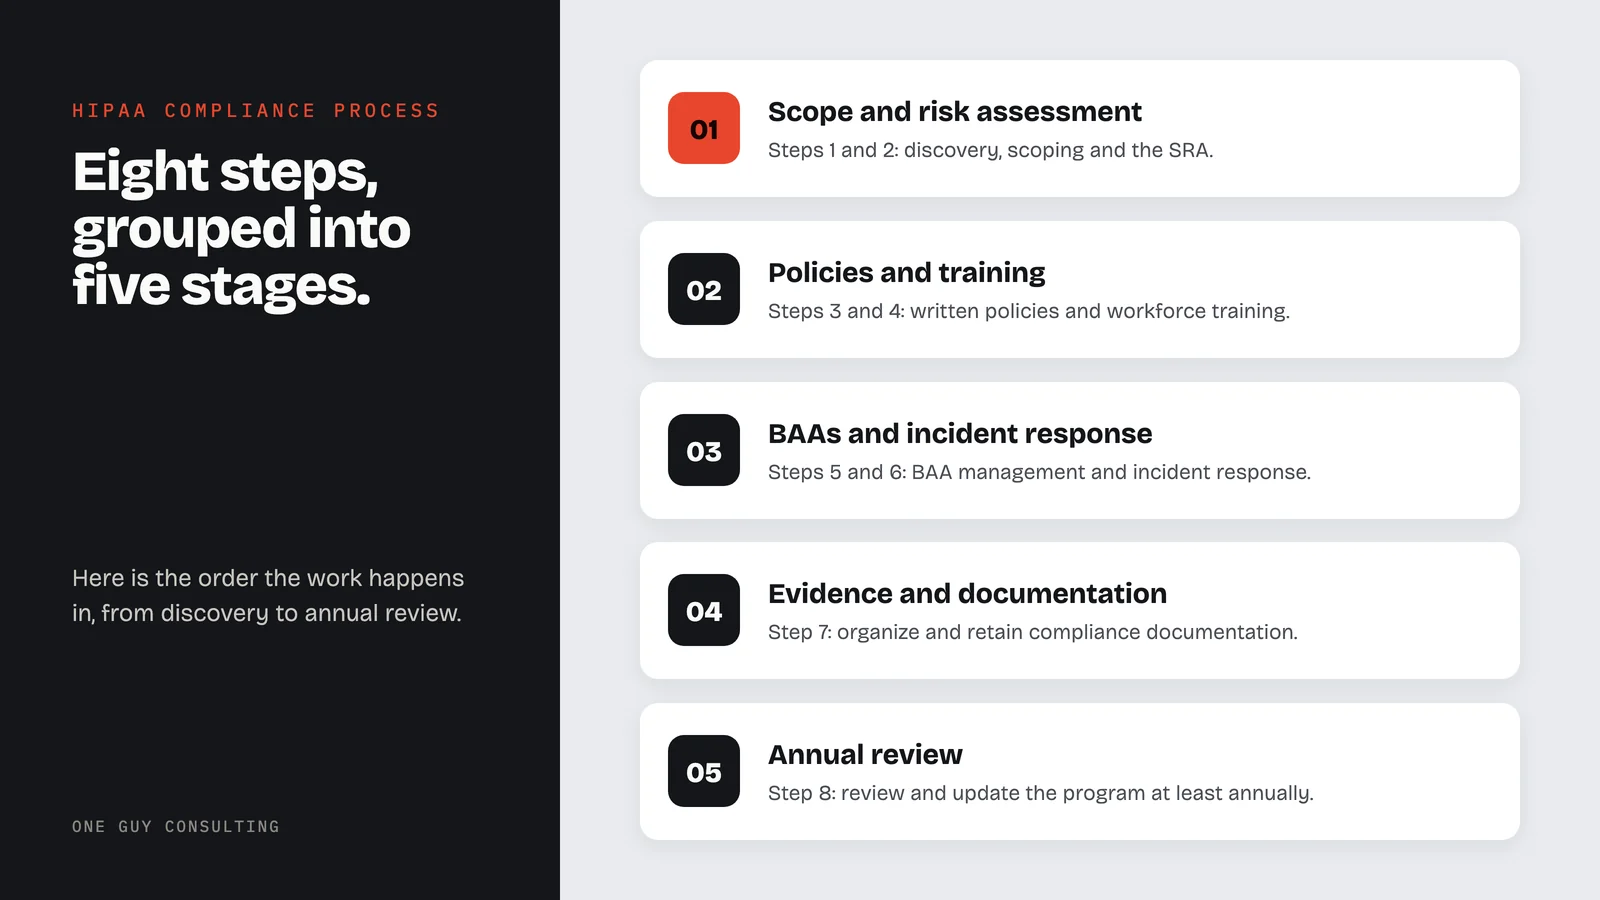
For a small practice with 1 to 25 staff members, the initial compliance process takes weeks, not months, when working with a consultant. Here is the order the work happens in:
Steps 1 & 2
Discovery, scoping, and Security Risk Assessment
Steps 3 & 4
Policy development and workforce training
Steps 5 & 6
BAA management and incident response planning
Step 7
Evidence packaging and documentation organization
Step 8
Annual review and continuous sustainment
Timelines vary based on practice size, complexity, and existing documentation. Larger organizations or those with multiple locations may need additional time.
Two Ways to Work Through This
Two plans, six ways to pay. No per-user fees.
Portal access with templates, training modules, and guided workflows. You work through each step at your own pace with built-in checklists and documentation tools.
View Plan DetailsA Certified HIPAA Professional walks you through every step. Includes your SRA, custom policies, staff training, BAA review, and ongoing support, with 4 hours a month of 1:1 implementation calls with Chuck.
View Plan DetailsSecure checkout by Stripe. Your payment details go straight to Stripe and never touch our servers.
HIPAA Compliance Process FAQ
What are the steps to HIPAA compliance?+
How long does HIPAA compliance take?+
What is the first step toward HIPAA compliance?+
Can a small practice achieve HIPAA compliance without a consultant?+
Ready to Start Your Compliance Journey?
One Guy Consulting works directly with small practices to build HIPAA compliance programs from scratch. A Certified HIPAA Professional walks you through every step.
Learn More About HIPAA Compliance
Explore Our Other HIPAA Services
This content is for educational and informational purposes only and should not be construed as legal advice.