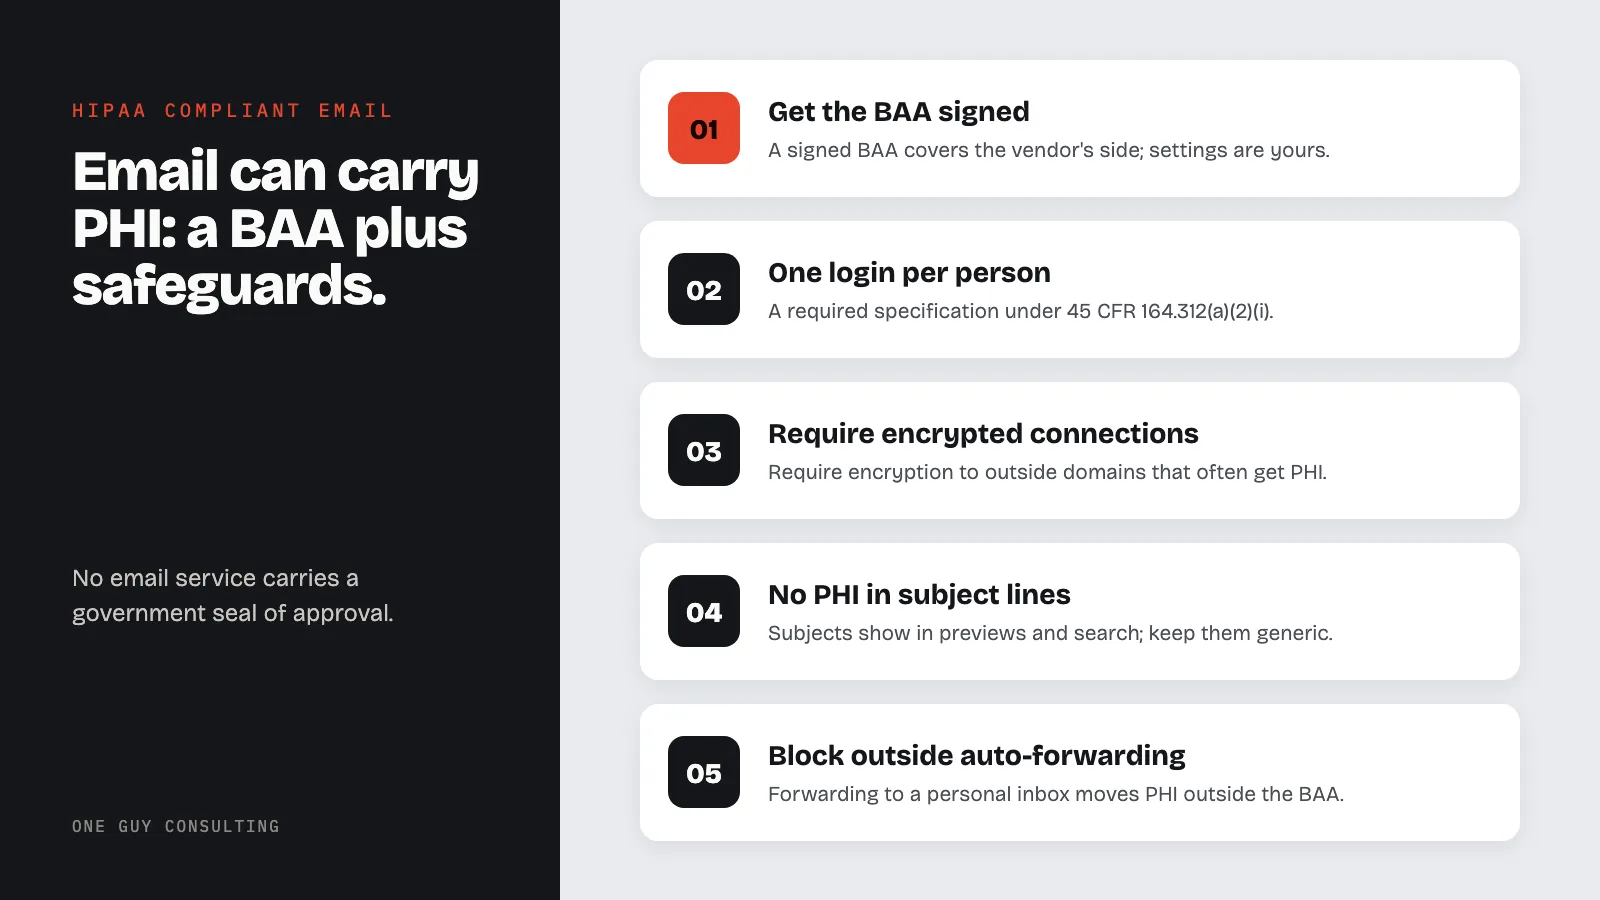
No email service carries a government seal of approval. HHS and its Office for Civil Rights state that they "do not certify any persons or products as 'HIPAA compliant.'" What makes HIPAA compliant email services usable for patient information is a Business Associate Agreement (BAA) signed by the provider, plus the encryption and access settings your practice turns on.
Google Workspace (not a free personal Gmail account) and Microsoft 365 both offer the BAA. Add-ons such as Paubox, LuxSci and Virtru, and separate services such as Hushmail and MailHippo, include one. This guide compares them by BAA, published price and how each works, then lists the settings a small practice turns on.
HIPAA Compliant Email Services: What Makes One Usable for PHI
A patient emails a photo of an insurance card. A referring office asks for a visit note. Someone on the front desk still forwards messages to a personal inbox. The question is not whether email is allowed. It is whether the email service in use is one the practice can put P.H.I. (Protected Health Information) through.
Two things decide it: a signed BAA with the email provider, and safeguards the practice has chosen and documented. Neither one comes from the brand name on the login screen.
What HIPAA Says About Email
HIPAA compliance for email starts with the HHS answer to a common question (HHS FAQ 570). HHS says providers may email patients, "provided they apply reasonable safeguards when doing so." The same answer says the Privacy Rule "does not prohibit the use of unencrypted e-mail for treatment-related communications between health care providers and patients."
The Security Rule sets the standard for electronic PHI in motion. Under 45 CFR 164.312(e)(1), a practice must "Implement technical security measures to guard against unauthorized access to electronic protected health information that is being transmitted over an electronic communications network." Email sent across the internet is exactly that.
Encryption sits under that standard as an addressable specification. The text of 45 CFR 164.312(e)(2)(ii) reads: "Implement a mechanism to encrypt electronic protected health information whenever deemed appropriate."
Addressable does not mean optional. Under 45 CFR 164.306(d)(3), the practice must "Assess whether each implementation specification is a reasonable and appropriate safeguard in its environment, when analyzed with reference to the likely contribution to protecting electronic protected health information." If the answer is no, the practice must "Document why it would not be reasonable and appropriate to implement the implementation specification" and "Implement an equivalent alternative measure if reasonable and appropriate." Separately, 45 CFR 164.308(a)(1)(ii)(A) makes a risk analysis a required specification: "Conduct an accurate and thorough assessment of the potential risks and vulnerabilities to the confidentiality, integrity, and availability of electronic protected health information held by the covered entity or business associate." For the fuller picture on encryption, see HIPAA encryption requirements.
Step 1: Get the BAA Signed
Under 45 CFR 160.103, a business associate includes a person who, on behalf of a covered entity and other than as a member of its workforce, "creates, receives, maintains, or transmits protected health information for a function or activity regulated by this subchapter."
Microsoft's HIPAA page describes its own role this way: "When a covered entity engages the services of a cloud service provider, such as Microsoft, the cloud service provider is a business associate under HIPAA."
Under 45 CFR 164.308(b)(1), a covered entity may let a business associate handle electronic PHI "only if the covered entity obtains satisfactory assurances, in accordance with § 164.314(a), that the business associate will appropriately safeguard the information." The Privacy Rule says the same for all PHI: 45 CFR 164.502(e)(1)(i) calls for "satisfactory assurance that the business associate will appropriately safeguard the information."
That assurance is the BAA. The HHS enforcement listing includes a 2017 case titled "No Business Associate Agreement? $31K Mistake" (April 20, 2017). The title says it plainly. For what a BAA has to contain, see what a HIPAA business associate agreement is.
How the two big platforms handle it, per their own pages (read September 29, 2026):
- Google Workspace. Google's HIPAA page says: "Customers who have not signed a BAA with Google must not use PHI in Google Workspace or Cloud Identity services." The BAA is made available for electronic acceptance in the Admin console. Google's HIPAA Included Functionality list, dated as of August 31, 2026, names Gmail, Google Calendar, Google Chat, Google Drive, Google Meet and Google Voice (managed users only), among others. Google also states that "Third-party applications including add-ons are not included in the Included Functionality covered by the BAA." Details: Is Google Workspace HIPAA compliant and Is Gmail HIPAA compliant.
- Microsoft 365. Microsoft's HIPAA page says its BAA "is available through the Microsoft Online Services Data Protection Addendum by default to all customers who are covered entities or business associates under HIPAA." Exchange Online is on its list of in-scope Office 365 services. Microsoft also says that using its services "doesn't on its own achieve HIPAA compliance." Details: Is Microsoft 365 HIPAA compliant.
Three Kinds of Service
Every option in this guide fits one of three shapes. The shape matters more than the logo, because it decides what staff have to learn and what a patient sees.
- The mailbox you already have, with its BAA. Google Workspace or Microsoft 365, once the BAA is in place and the settings are on. Nothing new to learn.
- An add-on to that mailbox. Paubox, the LuxSci Secure Email Gateway and Virtru sit on top of Google Workspace or Microsoft 365 and add encryption. Staff keep the inbox they know.
- A separate secure service. Hushmail for Healthcare is its own encrypted email service with its own mailbox. MailHippo says it "works with your current email address, and with any email provider"; recipients get a notice and open the message through a link on MailHippo's site.
The Comparison
Prices change. Check each vendor's page before buying.
| Service | Kind | BAA, per its own page | Published price | Works with |
|---|---|---|---|---|
| Google Workspace | Your mailbox | Accepted electronically in the Admin console | Not stated on its HIPAA page | Gmail is on the Included Functionality list |
| Microsoft 365 | Your mailbox | By default through the Data Protection Addendum, for covered entities and business associates | Not stated on its HIPAA page | Exchange Online is in scope |
| Paubox Email Suite | Add-on | "Paubox includes BAAs with all accounts" | Standard: $32 a month, up to 5 senders. Plus: $65. Premium: $75. All billed annually; its page also lists month-to-month prices. | Google Workspace and Microsoft 365; its page says "No portals or passwords needed for recipients" |
| LuxSci Secure Email Gateway | Add-on | BAA listed as included on every tier | $50 a month for up to 5 users | Microsoft 365, Google Workspace or on-premises email |
| Virtru | Add-on | Starter plan lists a "Signed Business Associate's Agreement (BAA)" | Starter: $119 a month, 5 users, billed annually | Google Workspace and Microsoft 365 (Gmail and Outlook); recipients need no new account |
| Hushmail for Healthcare | Separate mailbox | "Get a signed business associate agreement (BAA) for healthcare providers" | "Plans for as little as $11.99 per month" | Its own email service |
| MailHippo | Separate secure service | BAA listed on every plan | Basic: $4.95 a month for each user, billed annually ($59.00 a year), or $5.95 month to month. Pro: $7.95 billed annually ($95.00 a year), or $8.95. | Your current address; recipients open a link |
Paubox's side-by-side with One Guy Consulting is in Paubox compared. The table ranks nothing on purpose. The right service is the one that fits the mailbox a practice already runs and the risk analysis it has already done.
What a 5-Person Practice Pays
For a practice already on either platform, the BAA itself may cost nothing extra. Neither Google's nor Microsoft's HIPAA page lists a separate charge for the BAA. A practice on Google Workspace, or on a Microsoft business subscription covered by the Data Protection Addendum, already has the BAA on offer.
An add-on is a second line item on top of that subscription. The published entry points for five people, from each vendor's page:
- Paubox Standard: $32 a month billed annually, for up to 5 senders.
- LuxSci Secure Email Gateway: $50 a month for up to 5 users.
- Virtru Starter: $119 a month for 5 users, billed annually.
- MailHippo Basic: $4.95 a month for each user, billed annually, so the total depends on how many people send.
- Hushmail for Healthcare: a starting price of $11.99 per month on its healthcare page. Its pricing page asks how many email accounts are needed, so price all five accounts there.
Cheapest is not the only test. A standalone mailbox means staff check two inboxes. An add-on keeps one inbox but adds a second vendor, and a second BAA to keep on file.
Settings Checklist
A signed BAA covers the vendor's side. The practice's side is configuration. Phishing appears in HHS enforcement titles: the listing includes a $600,000 settlement titled "HHS Office for Civil Rights Settles Phishing Attack Breach with Health Care Network for $600,000" (April 23, 2025) and a $3,000,000 settlement with Solara Medical Supplies from a HIPAA phishing cybersecurity investigation (January 14, 2025).
The settings below are common ones. Where a setting ties to rule text, that text is cited with it.
- One login per person. 45 CFR 164.312(a)(2)(i) is a required specification: "Assign a unique name and/or number for identifying and tracking user identity." No shared front-desk mailbox password.
- TLS enforced for regular outside recipients. Where the service offers it, require an encrypted connection to the outside domains that receive PHI often (labs, referring offices, billing). This is a technical security measure a practice can weigh under the transmission security standard in 164.312(e)(1).
- Two-step sign-in on every mailbox. Multi-factor authentication is a safeguard supporting 45 CFR 164.312(d), which says to "Implement procedures to verify that a person or entity seeking access to electronic protected health information is the one claimed." The current rule does not name MFA; making it mandatory is part of the 2025 proposal described below.
- No PHI in subject lines. Subject lines show up in previews, notifications and search. Keep them generic.
- Auto-forwarding to outside addresses turned off. A rule that copies work mail into a personal inbox moves PHI outside the BAA.
- Records kept 6 years. Under 45 CFR 164.316(b)(2)(i), Security Rule documentation is kept "for 6 years from the date of its creation or the date when it last was in effect, whichever is later." That can include the email policy, the encryption decision and the BAA itself.
One Guy Consulting's compliance software includes vendor management with automated contract execution (digital BAAs) on both plans. On the Full-Scope plan, Chuck "Answers vendor questions you have + aids technologically as needed with regard to the vendor profile."
Patients Who Want Plain Email
Some patients ask the office to just email it. The rule gives patients a voice in how they are contacted. Under 45 CFR 164.522(b)(1)(i), "A covered health care provider must permit individuals to request and must accommodate reasonable requests by individuals to receive communications of protected health information from the covered health care provider by alternative means or at alternative locations."
The practice may require that request in writing. 45 CFR 164.522(b)(2)(i) says: "A covered entity may require the individual to make a request for a confidential communication described in paragraph (b)(1) of this section in writing."
HHS FAQ 570 is the source for unencrypted email with patients, quoted above: it is not prohibited for treatment-related communications, with reasonable safeguards. What a practice tells a patient about the risks, and how it records the patient's choice, is a policy decision. Questions about a specific consent form belong with a healthcare attorney. The same logic applies to text messages; see the HIPAA texting rules for patients.
The Proposed Security Rule and Email
On January 6, 2025, HHS published a proposed rule to update the Security Rule (90 FR 898). It is not final. HHS's regulatory agenda now lists the final action for July 2027, and the current Security Rule, with its required and addressable split, still applies.
Among its proposals, the NPRM describes "expressly requiring regulated entities to encrypt ePHI, with limited exceptions," and it proposes multi-factor authentication. Both are proposed, not law, and nothing is required today because of the proposal alone. More on email and security questions sits in the HIPAA security FAQ.
This article is educational and is not legal advice.
FAQ
Is there a free HIPAA compliant email service?
Not among the paid add-ons and separate services in the table: each pricing page read on September 29, 2026 lists paid plans, though MailHippo's also lists a 30-day trial tier that includes its BAA. A free personal Gmail account is a different case: Google's route to a BAA for Gmail is a Google Workspace account, with the BAA accepted in the Admin console.
What is the cheapest HIPAA compliant email for a small practice?
It may be the one already paid for. Google Workspace and Microsoft business subscriptions under Microsoft's Data Protection Addendum both offer a BAA, and neither HIPAA page lists a separate charge for it. Among the add-ons and separate services, the lowest published entry points on September 29, 2026 were MailHippo Basic at $4.95 a month for each user, billed annually, and Hushmail for Healthcare plans from $11.99 per month.
Is there HIPAA compliant email for therapists?
The rules are the same for a therapy practice as for any covered health care provider: a BAA with the email provider, and safeguards chosen in the risk analysis. Every service in the table above lists a BAA on its own page, and Hushmail markets a healthcare plan that includes one.
Is regular email HIPAA compliant if the patient asks for it?
HHS FAQ 570 says the Privacy Rule does not prohibit unencrypted email for treatment-related communications between providers and patients, provided reasonable safeguards are applied. The same HHS answer adds that covered entities "will want to ensure that any transmission of electronic protected health information is in compliance with the HIPAA Security Rule requirements." Under 45 CFR 164.522(b)(1)(i), a provider must accommodate reasonable requests to communicate by alternative means. How the practice records that request is a policy decision; a healthcare attorney can review the wording.
Does Gmail or Outlook count as HIPAA compliant email?
Gmail inside Google Workspace is on Google's HIPAA Included Functionality list once the BAA is accepted. For Outlook, what counts is the account behind it: Exchange Online is on Microsoft's list of services in scope for its BAA. Neither company's HIPAA page describes a BAA for a personal consumer mailbox. The BAA applies once it is in place, and the settings are the practice's own work.
Email can carry PHI when the provider has signed a BAA and the practice has turned on the safeguards its risk analysis calls for. A practice that already pays for Google Workspace or a Microsoft business subscription may find the BAA already on offer; the next question is whether an add-on is worth its published price.
Want help putting this in place? The Full-Scope plan from One Guy Consulting pairs the compliance software with 4 hours a month of 1:1 implementation calls with Chuck Weiselberg, C.H.P., to get your plan set up, with no per-user fees. See how it works or book a free HIPAA compliance review. No obligation, no pressure.
Sources
- 45 CFR 160.103 (definitions: business associate)
- 45 CFR 164.312 (technical safeguards)
- 45 CFR 164.306 (security standards: general rules)
- 45 CFR 164.308 (administrative safeguards: risk analysis, business associate contracts)
- 45 CFR 164.314 (business associate contracts: requirements)
- 45 CFR 164.316 (documentation and retention)
- 45 CFR 164.502 (disclosures to business associates)
- 45 CFR 164.522 (confidential communications)
- HHS FAQ 570: Does HIPAA permit health care providers to use email to discuss health issues with patients
- HHS OCR: Be aware of misleading marketing claims
- HHS OCR Resolution Agreements and Civil Money Penalties (enforcement listing)
- Federal Register, HIPAA Security Rule To Strengthen the Cybersecurity of Electronic Protected Health Information (proposed rule, 90 FR 898, January 6, 2025)
- Unified Agenda, RIN 0945-AA22, HIPAA Security Rule (reginfo.gov, fetched 2026-09-29)
- Google Workspace: HIPAA compliance with Google Workspace and Cloud Identity (fetched 2026-09-29)
- Google Workspace: HIPAA Included Functionality, as of August 31, 2026 (fetched 2026-09-29)
- Microsoft Learn: HIPAA and HITECH Act offering (fetched 2026-09-29)
- Paubox Email Suite pricing (fetched 2026-09-29)
- LuxSci pricing (fetched 2026-09-29)
- LuxSci Secure Email Gateway (fetched 2026-09-29)
- Virtru pricing (fetched 2026-09-29)
- Virtru HIPAA email (fetched 2026-09-29)
- Hushmail for Healthcare (fetched 2026-09-29)
- Hushmail pricing (fetched 2026-09-29)
- MailHippo pricing (fetched 2026-09-29)
- MailHippo home page (fetched 2026-09-29)
Related Reading