There is an impression in the marketplace that it costs an arm and a leg to become compliant with HIPAA. While you could certainly buy your way towards a compliant status, this is not a realistic option for most. So, in lieu of funds and the ability to hire a third-party who can seamlessly handle every tiny facet of your compliance plan, we get creative! Below I will explain how to become HIPAA compliant without breaking the bank.
Quick Note:
While I will discuss below some thrifty ways to satisfy various requirements of the HIPAA law, this article is no substitute for seeking the advice of an Attorney who can specifically address the unique concerns of your organization.
With that disclaimer posted, my first low-cost step for small clinics becoming HIPAA compliant in 2027 is about… Drum roll pleaseeee……
Alarm Systems
Now, when I say alarm system right out of the gate you may say to yourself, “What is this guy talking about? Those aren’t low-cost!” And you would be right to think this way. But, set aside thoughts of a fancy third-party company, with agents ready to help you 24/7, and a little shield on a stick to put in your yard for a moment. Instead of going that ‘boutique’ security route, why don’t we check what the actual law says first? The section of the Security Rule on Facility Access Controls (45 CFR 164.310(a)(1)) states you are in compliance when you,
- “Implement policies and procedures to limit physical access to its electronic information systems and the facility or facilities in which they are housed, while ensuring that properly authorized access is allowed.”
In plain English this says you need to have written policies and procedures on how you intend to protect both PHI and the building it lives in through tangible, physical means. One great way to approach that is to purchase an inexpensive, motion-sensor camera (or cameras) to point at your most active doorways and entrances. Ideally, the camera came with an app for your cell phone which will ping you directly if the motion sensor is tripped during off-hours of your choosing. This way, if someone does break in, you can call the Police for assistance right then and there. The best part is that the set-up can cost you a mere $15.99 if you were to place an order for this Blink brand security camera in the very near future (It’s a flash sale!).
A Well-Trained Staff
Holding regular staff training sessions sounds like an ‘out there’ thing to list in this article, but human error is the root cause of so many more unauthorized disclosures of PHI than anything else, I’d be remiss to not point out the savings (financially) to be had from a well-trained staff. Even if HIPAA training costs your organization some nominal amount, it pays dividends the moment it prevents an astronomically expensive fine from being levied against your organization when someone goofs up one day. Train often and train well to mitigate concerns about staff following the law.
One Guy Consulting
Linking up with One Guy Consulting to help you establish your HIPAA compliance plan is one of the best low-cost moves you can make for the sake of your small clinic for 2027. One Guy Consulting goes to great effort to ensure our rates fall well below the rates charged by competitors in this same niche. One Guy Consulting is wholly committed to providing you with a HIPAA compliance solution that is low cost, but never low quality.
As One Guy Consulting expands further into the world of cybersecurity, the value of keeping everything in one centralized location is top of mind, but not top of wallet.
Here is a quick refresh of the low-cost services we provide + some cybersecurity offerings that are being rolled out shortly:
- Full-Scope Plan for total HIPAA Compliance ($1,300 a year, or $120 a month)
- Mobile Device Management is available for only $15 per device, per month
- Managed Security Monitoring (MSM) - This service is intended to provide subscribers with continuous monitoring against active threats and vulnerabilities at a fraction of the price it would cost for you to retain the services of a traditional MSP. The cost for MSM service is device dependent:
- Up to 5 devices = $99 / Mo.
- 6 to 15 devices = $199 / Mo.
- 16+ devices = $349 / Mo.
- Penetration testing is coming soon! I have been head’s down on that piece for a moment and think it is really starting to progress in the right direction quite nicely. Stay tuned for pricing news and everything else to do with this part of our forthcoming cybersecurity offering.
- Vulnerability Scanning - What better way to prepare for 2027 than trying to guess when in July the government might mandate this scan as part of a sweeping update (possibly) to the security rule? Well, whenever you get around to looking into this further, please feel welcome to drop me a line, as this service is up and ready.
I will be offering two different types of vulnerability scanning. The buzz on the street is that, if finalized in July, the government will be mandating such a scan be conducted every 6 months. If this ends up being the case, I have your back for the year for only $750 (Not $1500, mind you - $750 for both tests 6 months apart).
Option two for vulnerability scanning was built with my fellow small business owners in mind. It is especially awesome if you are a one-person operation. You can purchase a one-time trial scan, to be performed once, on one computer for only $59. Why such a difference? My hope is that you will trial the service and it will perform so far beyond your expectations, you make the leap to an annual subscription.
My favorite part of the trial scan offer is that it can be purchased and running on your computer entirely at a time of your choosing. It’s so dead simple, you can run it half-asleep at 3 AM if you wanted. What’s even slightly cooler is that there’s no ‘uninstall shuffle’ you need to do, since the agent dropped onto your device will self-destruct in 3 days’ time.
We’ve been focusing on low-cost measures to become HIPAA compliant, but how about everyone’s favorite fiscal term, ‘FREE’? Full Disk Encryption for your computer doesn’t cost you a dime.
If you use a PC, write down the name BitLocker. If you are more of a Mac person, the name FileVault may ring familiar. FileVault and BitLocker are applications that come with your computer. No separate hardware is necessary. There is no need for technical wizardry. For once, it really is as easy as flipping the proverbial switch to protect your device.
By enabling FileVault or BitLocker your computer’s entire hard disk becomes encrypted on the spot. This means that if a malicious actor DID gain access to your device you’d still be safe, since the attacker will only see jargon and not sensitive PHI.
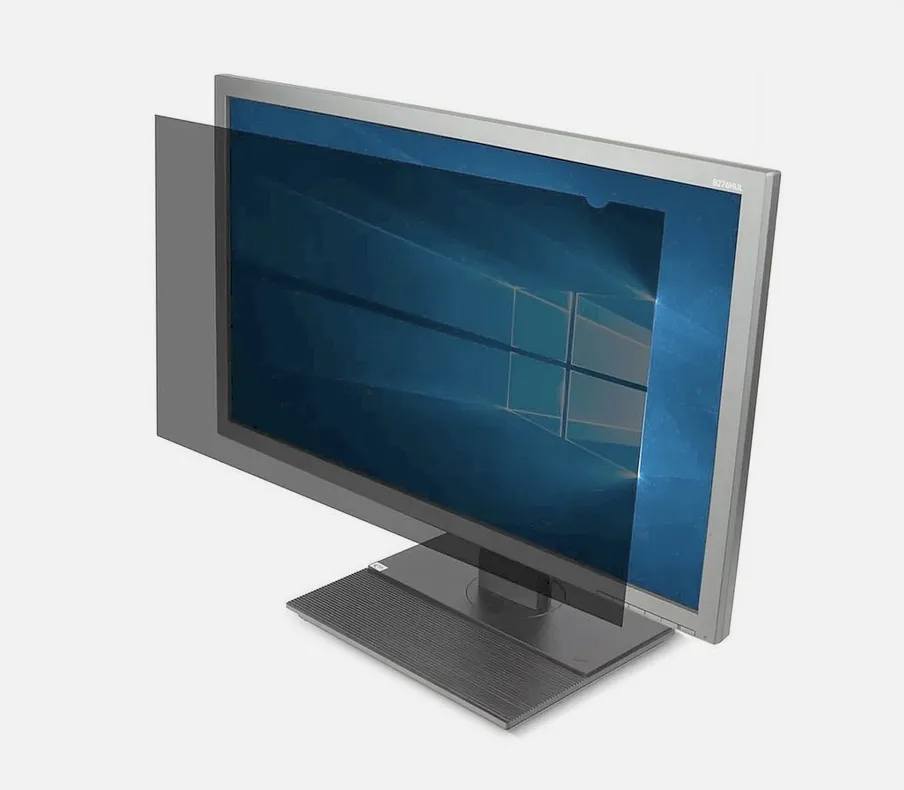
Sticking with computers for a moment, but considering them through the lens of physical safeguards, we need to give consideration to the actual device most capable of divulging PHI by accident; your monitor. If you think back to the last time you were at the Doctor for an appointment I’m sure you will recall the privacy screen on said monitor. To be specific, a privacy screen for your computer monitor makes it impossible to read what is on-screen unless you are directly in front of it. This clever way of keeping nosy folks out of others’ business deserves a special shout-out for its savings potential. With screens like this one setting you back a whopping $35, how could you not snag several at once?
Mobile Device Management, or MDM, is a great technical safeguard that is low-cost and worth the investment. With MDM, you can remotely enforce policies that have to deal with access controls, minimum necessary standards, patching software and OS updates automatically, and loads more.
If someone loses a device which was logged into a system containing ePHI, MDM enables you to wipe the memory of that device. Obviously, that is a last ditch effort, but it’s reassuring to know that in a worst case scenario you can instantly eliminate all traces of ePHI on a device that gets stolen from or lost by an employee. There’s much more MDM can do, but in the interests of time I’ll leave you to look into that one on your own.
Thanks so much for stopping in to read this article on the top 7 low-cost steps for small clinics becoming HIPAA compliant in 2027. I hope you have found this countdown to be helpful to you in your compliance journey! If you have any questions, please email me. I’m happy to help!
Try three One Guy Consulting 3D staff training courses free →